Introduction
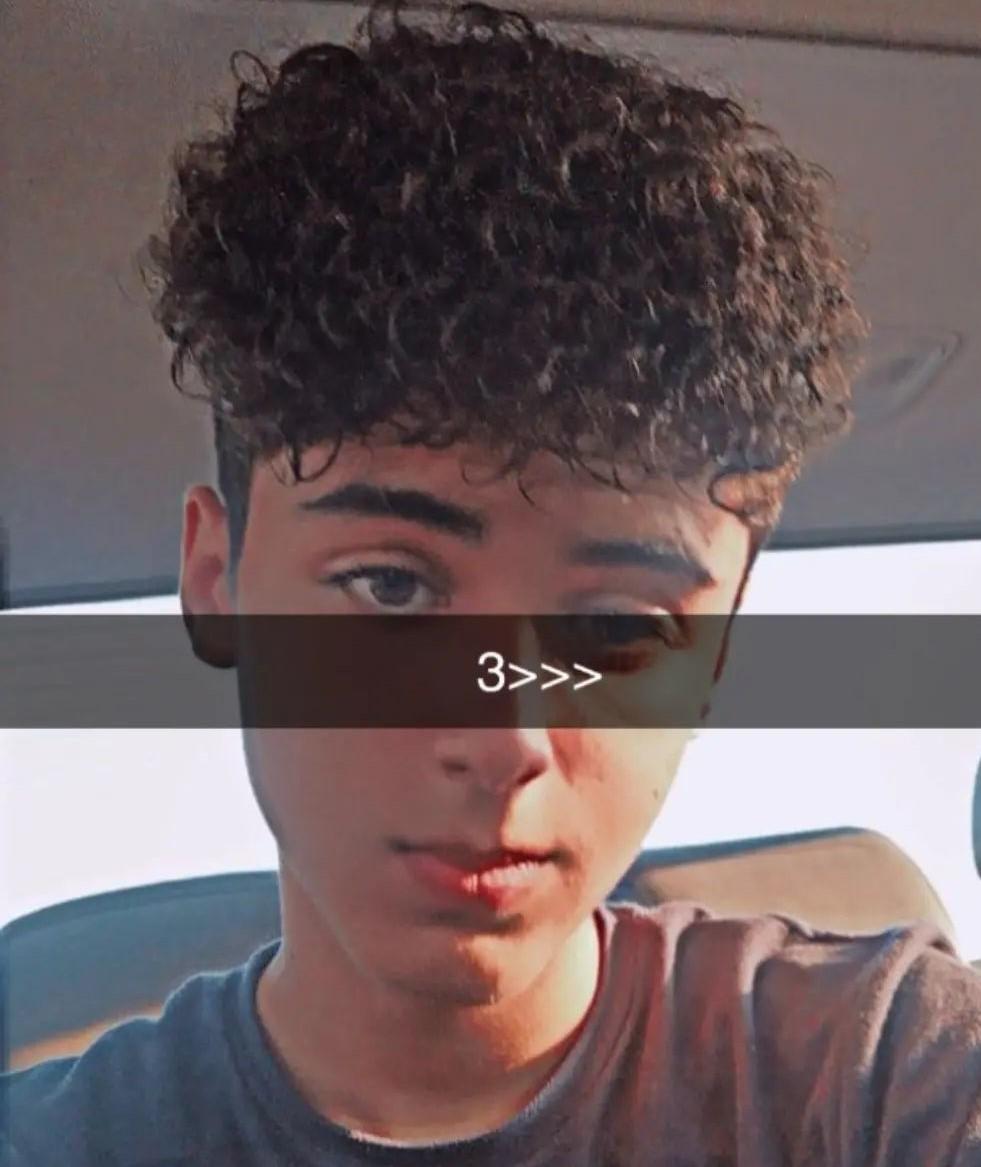
This is pryx as a young skiddie 3>>> Pryx enjoys gaming (Grand Theft Auto, WatchDogs, Mad Max), anime, hentai and music by Michael Ramir C. He is learning Java and selling game cheats and trolling. Pryx starts cybercrime at 12 years and pryx (like his best friend Rey) enjoys stealing his mother's identity for cybercrime.
Why do these skiddies use their mothers for cybercrime?
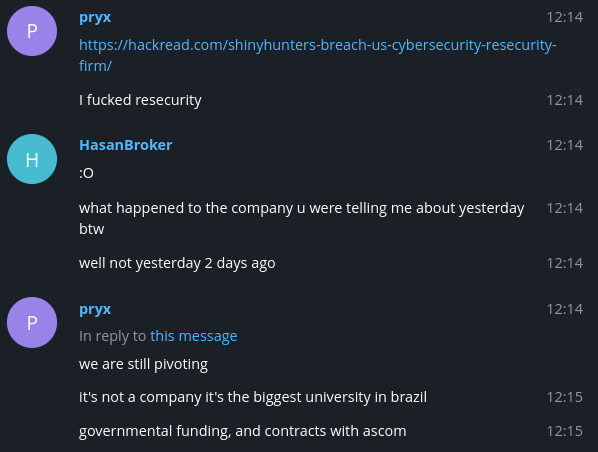
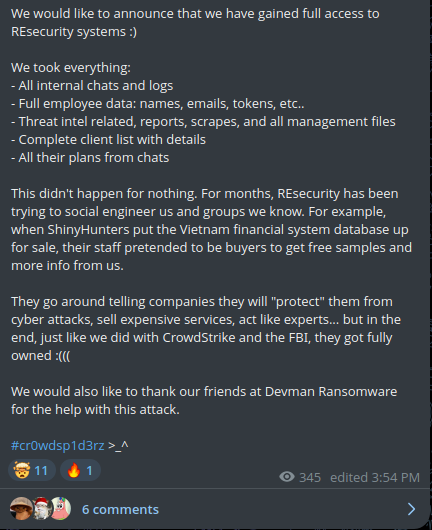
Scattered LAPSUS$ Shiny Hunters was caught in a honeypot by REsecurity and claimed responsibility. Privately pryx claimed "I fucked resecurity" and self attributed. This and other evidence places him as a member of SLSH and eligible for a 15 BTC self-imposed bounty.
|
|
|
Let us dive in.
ICA Group
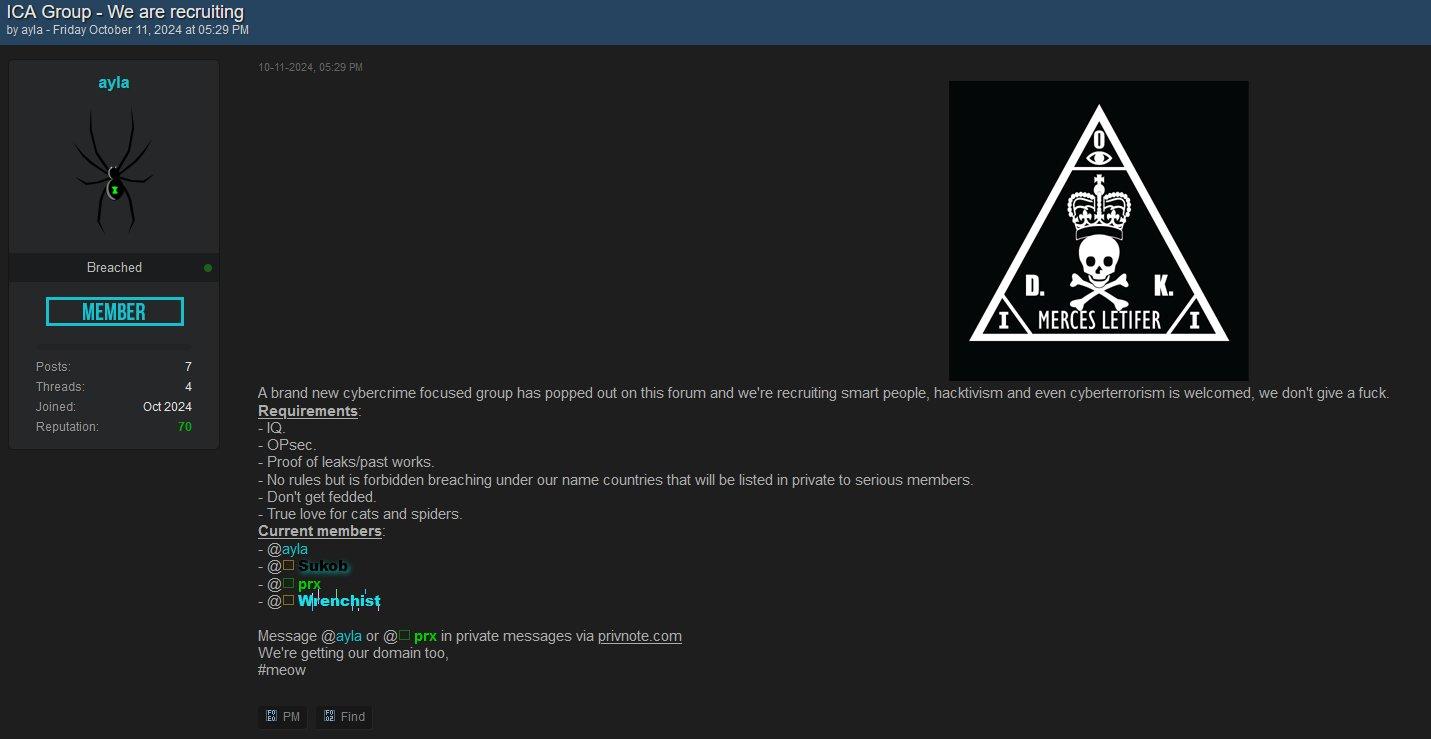
Brand new ICA Group emerged in late 2024 recruiting members with proof of prior breach and OpSec 🤣 Sophisticated threat actors always practice good opsec as you know from our prior articles.
Group members: Ayla, Sukob, prx, Wrenchist.
One of these members is grep and another is Rey, as told by pryx in this interview by OSINT10x
Pryx: Hellcat started as a joke when my friend Grep made a comment in the BreachForums shoutbox during a conversation about ICA.gov. He said, “ICA is a cool name for a group.” I sent him a private message saying it wasn’t a bad idea. We planned it out and announced it on BreachForums. Later, we found out ICA was linked to an Iranian ISIS group, so we changed the name to “Hellcat,” which was suggested by a member of the group named Rey
This group accomplishes nothing and quickly rebrands into:
Hellcat
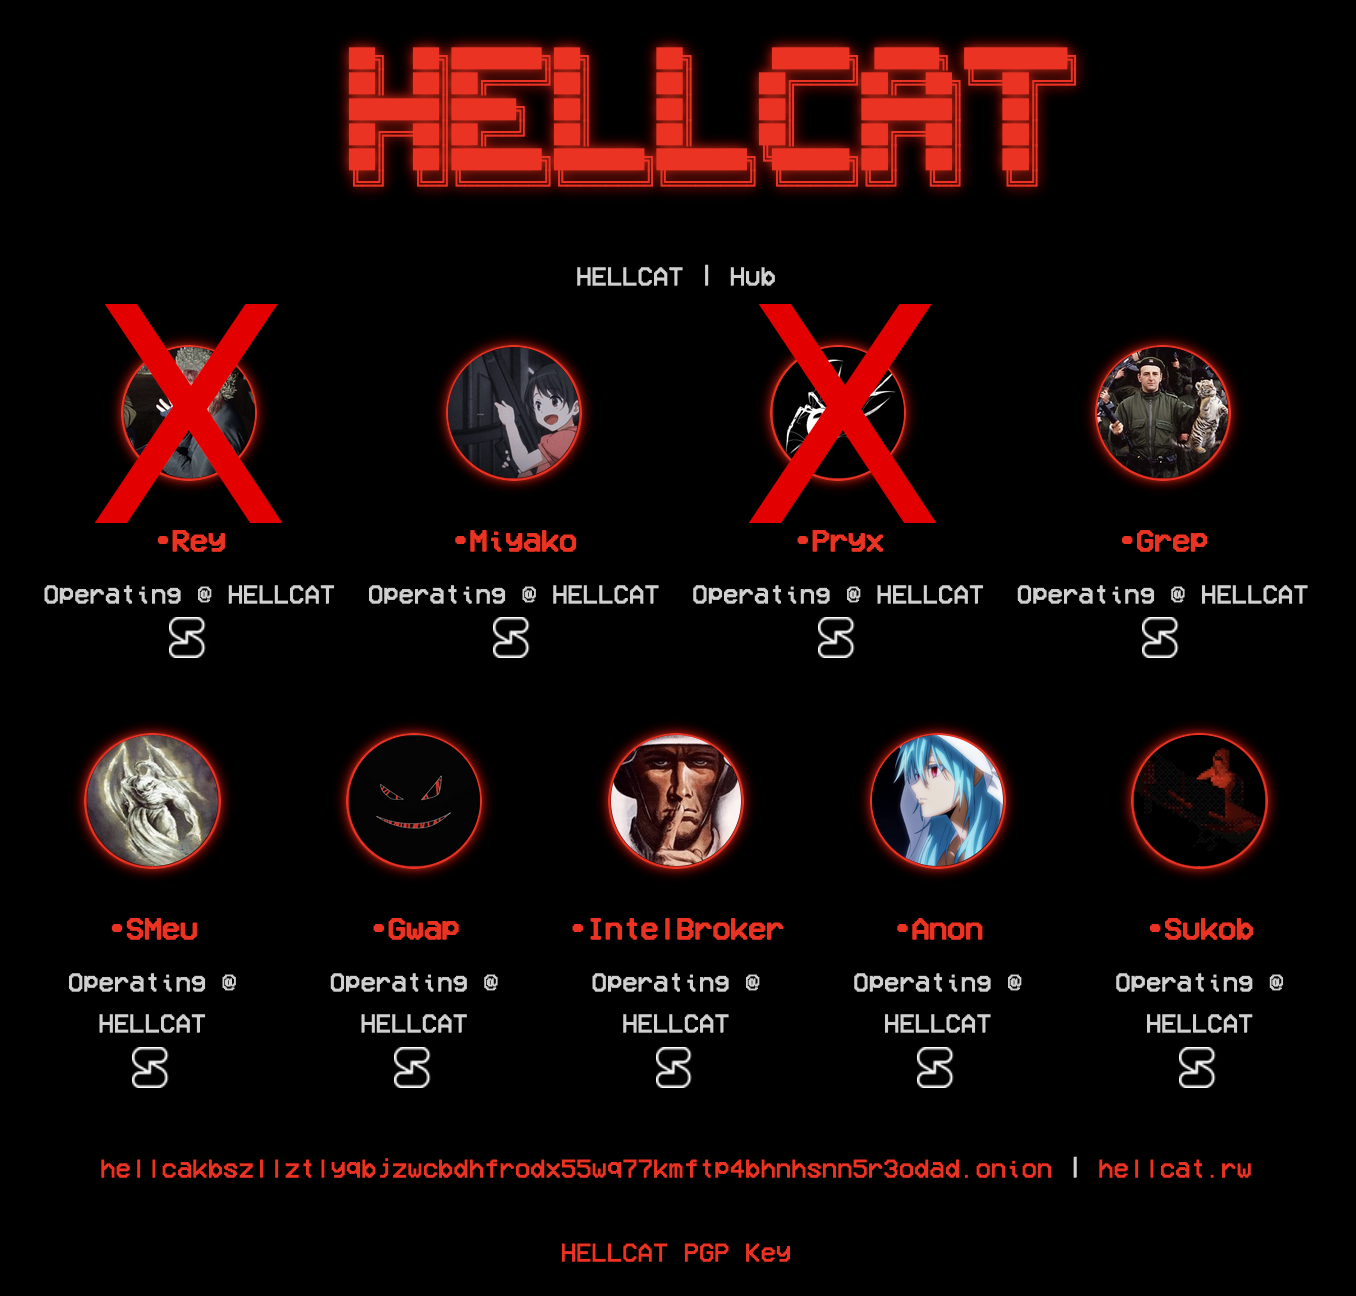
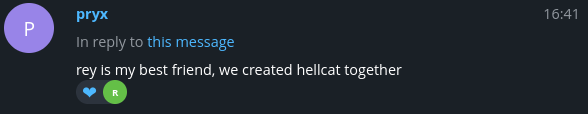
"Rey is my best friend, we created hellcat together" pryx claims
Hellcat employs phishing and ransomware and “Humiliation is a major psychological tactic leveraged by Hellcat,” Does this sound some how familiar?
Pryx claims to have disbanded Hellcat. We believe this is because Hikki-Chan Rey and Hellcat started to earn a poor reputation.
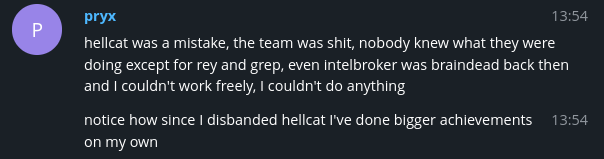
Pryx shit talks on Hellcat
"Hellcat was a mistakte" says pryx. "The team was shit"
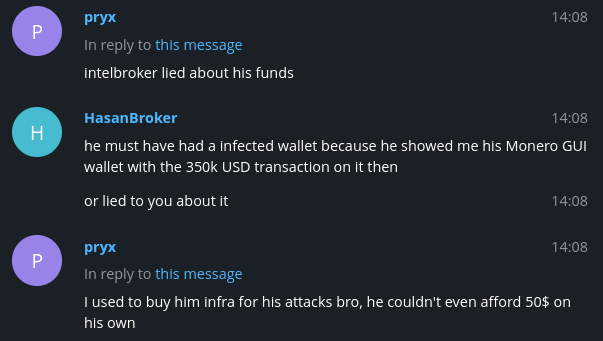
"IntelBroker lied about his funds. I used to buy him infra for his attacks bro"
Pryx Likes Forums
Pryx is a user on many english and Russian cybercrime forums. Pryx was banned on the original BreachForums reason: Arrested ("Some shit happened, but no I don't want to get into it" says pryx)
Previous to the pryx username he also was called WeedByte and Weed
Pryx worked on DangerZone forum and others and was a big hand in the launch of Hasan's Breachforums clone.
|
|
|
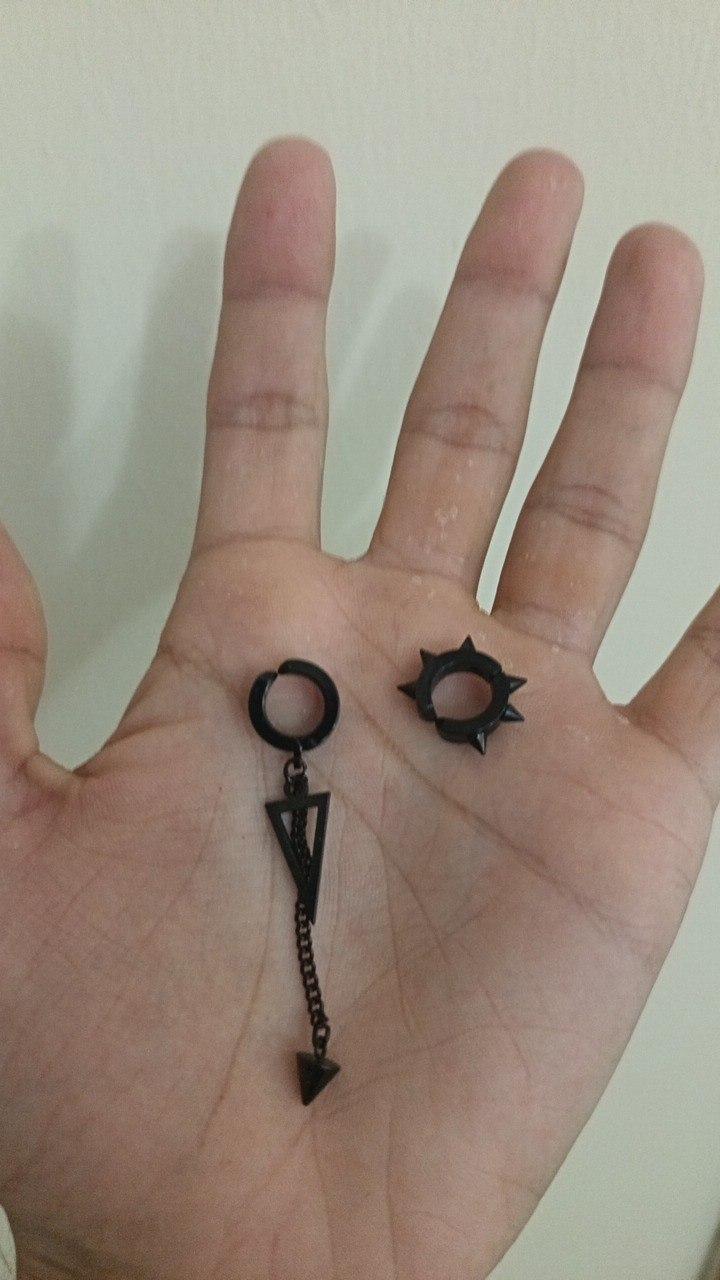
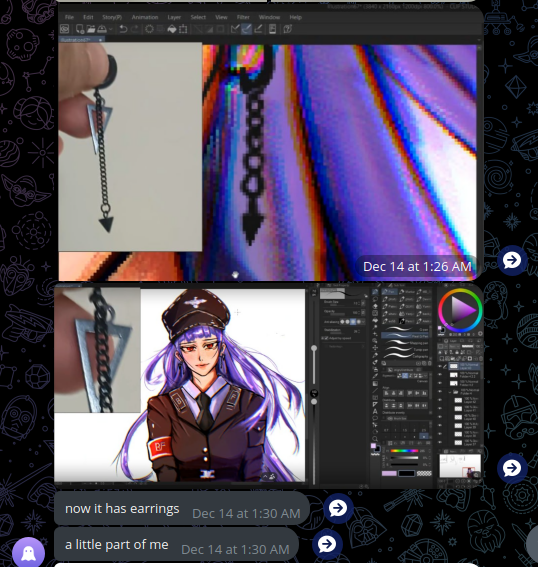
Pryx had a hand in the Hasan Breachforums clone and the design of the mascot. "Now it has earrings, a little part of me" says pryx. Remember these earrings, it will be important coming up.
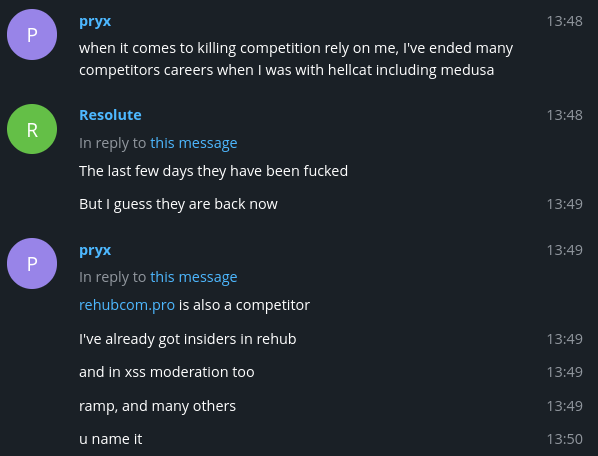
Hasan's BreachForums admin chat was leaked and in this chat pryx talks about killing competition. Pryx brags about killing Medusa and other competitors. Pryx claims to have insiders inside rehub, XSS mods, RAMP and many others.
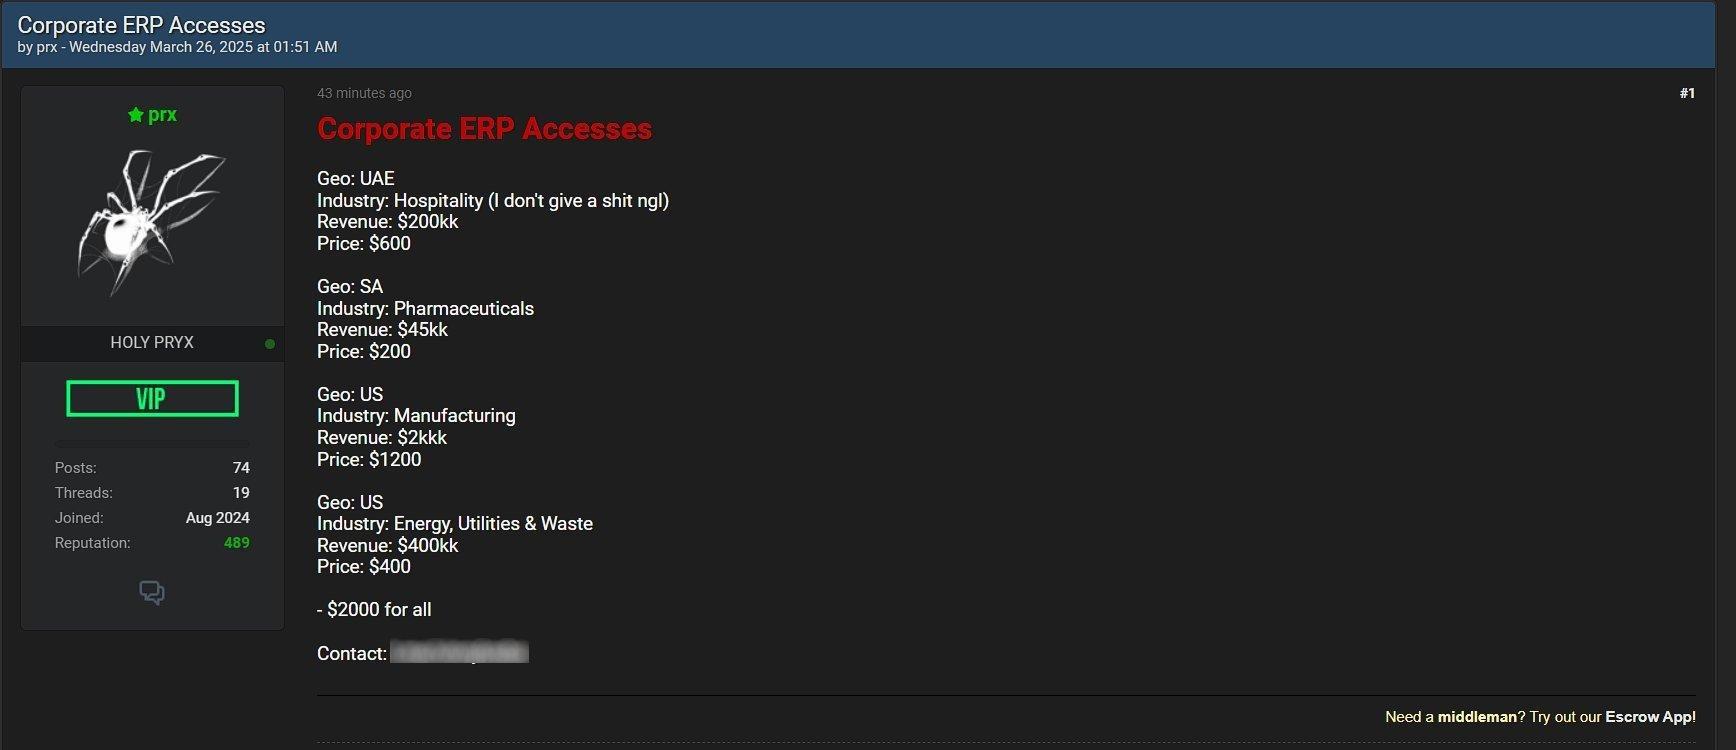
Pryx also sells initial access on forums including Hospitality and states he does not give a shit.
Pryx loves to brag
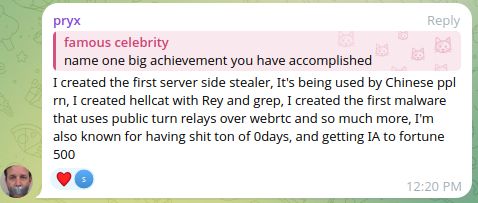 "I created the first server side stealer, It's being used by Chinese ppl rn"
"I'm also known for having shit ton of 0days, and getting IA to fortune 500"
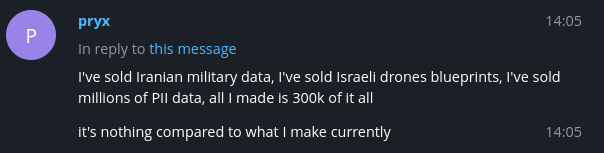
"I've sold Iranian military data ... Israeli drones blueprints ... millions of PII data, all I made is 300k of it all. It's nothing compared to what I make currently"
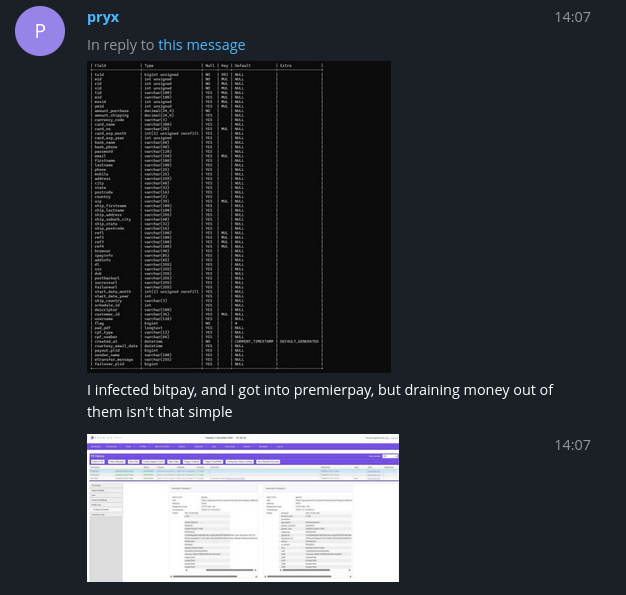
"I infected bitpay, and I got into premierpay" but pryx was unable to steal funds.
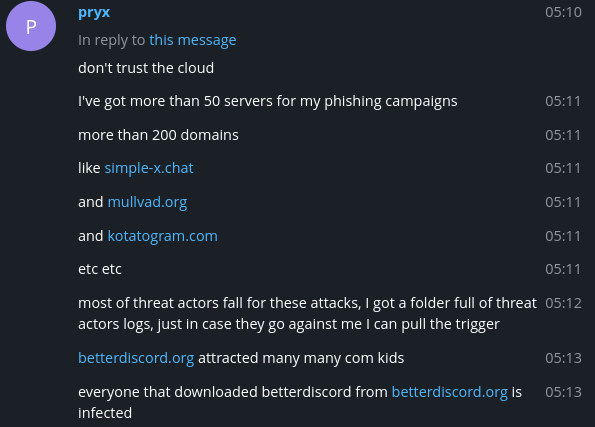
"Don't trust the cloud" pryx warns. Pryx claims many threat actors and com kids fell for his traps.
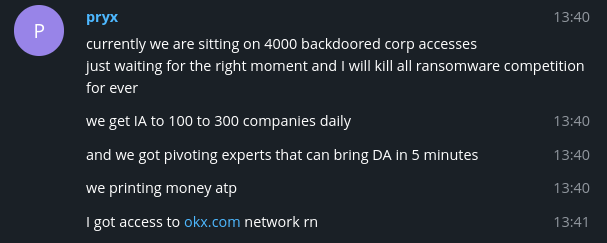
"Currently we are sitting on 4000 backdoored corp accesses, just waiting for the right moment and I will kill all ransomware competetion for ever"
"we printing money at this point"
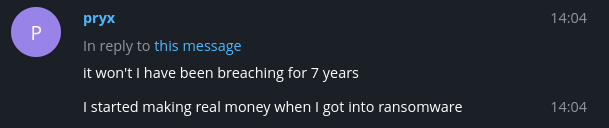
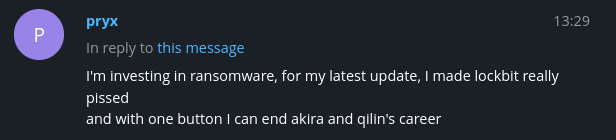
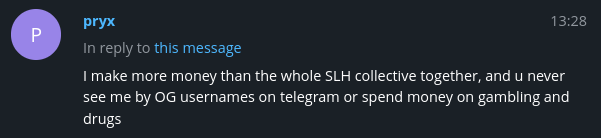
Pryx has been breaching and hacking since he was 12. He is investing and pivoting into ransomware and brags about making more money than the whole SLSH collective together.
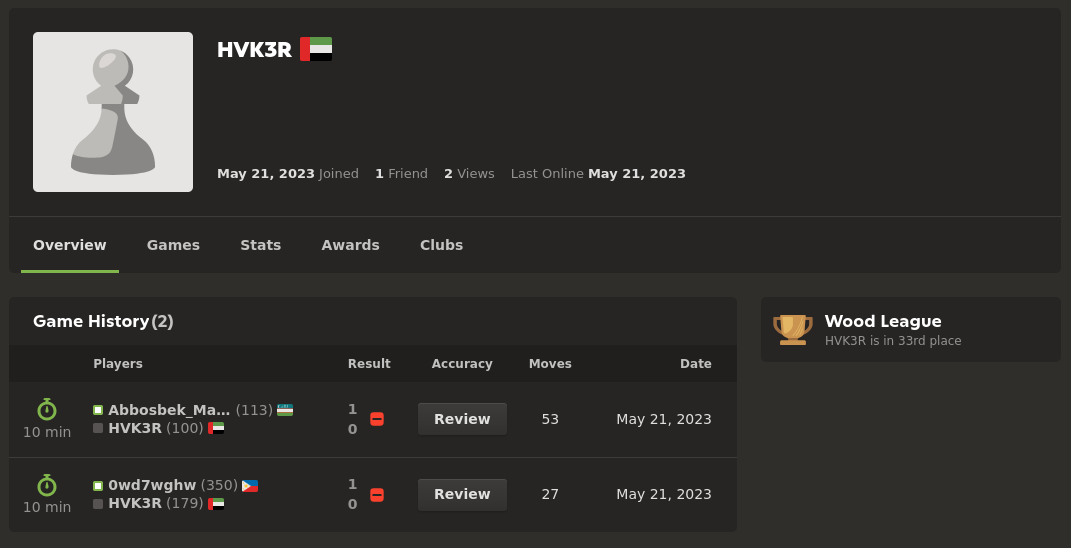 https://www.chess.com/member/hvk3r
HVK3R tried out some games of chess, but was not very good and gave up after two losses. He does not brag about his chess skills.
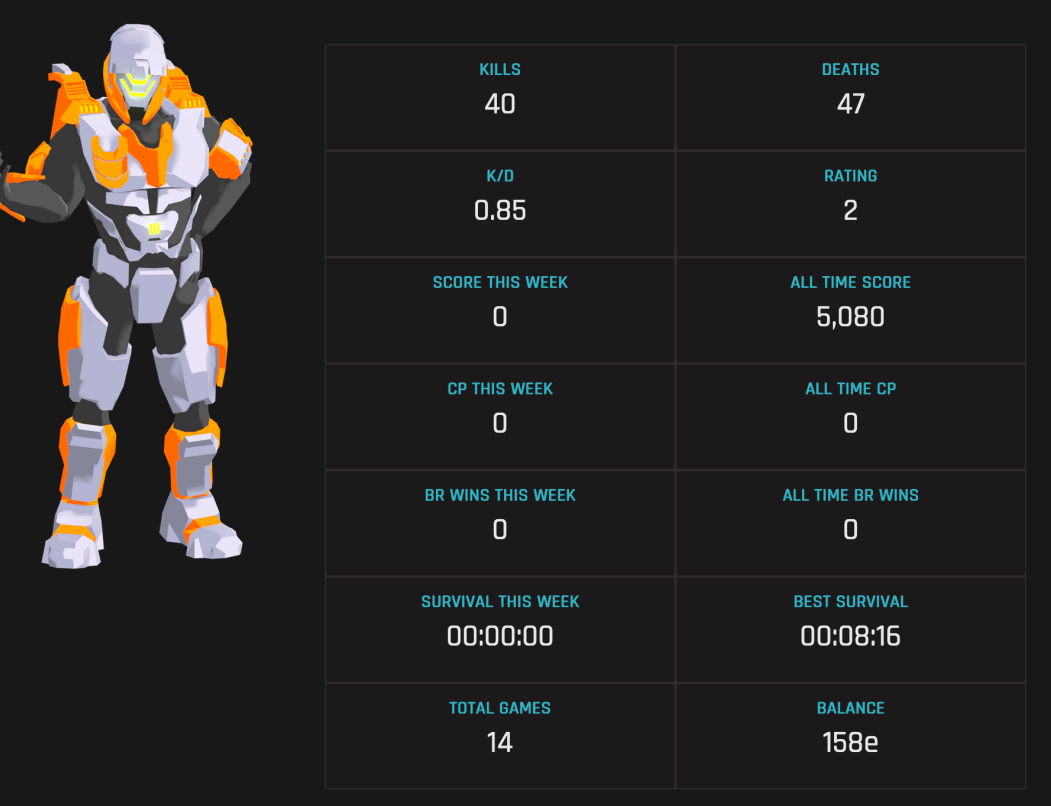
Neither does Pryx brag about his stellar kill death ratio on ev.io
Pryx biggest brag? Murder.
Pryx stole his mother's identity
Stealer logs share with us the password of Pryx: KIARIO123. We compare it with the password of his mother Saoussen El Adeb. We find that pryx stole his own mothers identity for a Binance account. Perhaps this account was used to launder illicit cybercrime funds.
URL: https://discord.com/login
Username: adameladeb2007@gmail.com
Password: KIARIO123
URL: https://accounts.binance.com/en/register
Username: saousseneladeb@gmail.com
Password: KIARIO123
Pryx also uses his mothers identity for accounts on discord, roblox, honeygain, nintendo and google.
Sophisticated threat actors use long, random, complex and strong passwords such as KIARIO123 to thwart brute force password cracking
Have a giggle at some of pryx secure passwords: KIARIO123 ADAMGOOGLE! ADAMPAYPAL! ADAMSPOTIFY! Even the seasoned investigators amongst our readers will no doubt have troubles deciphering what services these secure passwords unlock.
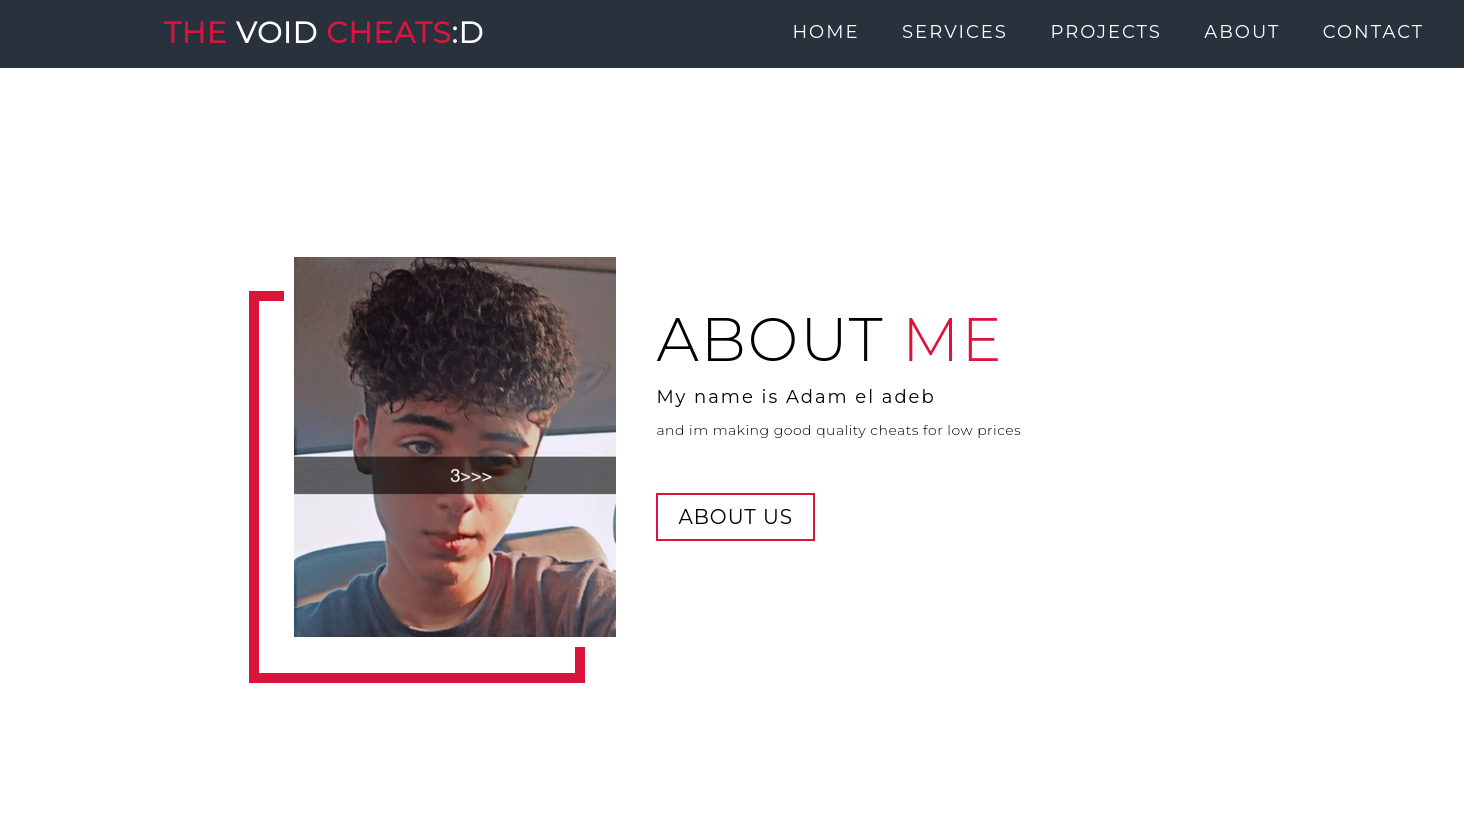
My name is Adem El Adeb
https://adameladeb.github.io/The-Void-Hacks.com/#about
Adem is 18 years old, born in 2007. Adem is Tunisian, ethnic Berber Amazigh. Adem is from Ras Al Khaimah. RAK is an industrial port city and the largest city and capital of the Emirate of Ras Al Khaimah in the UAE.
Pryx began his breaching career here
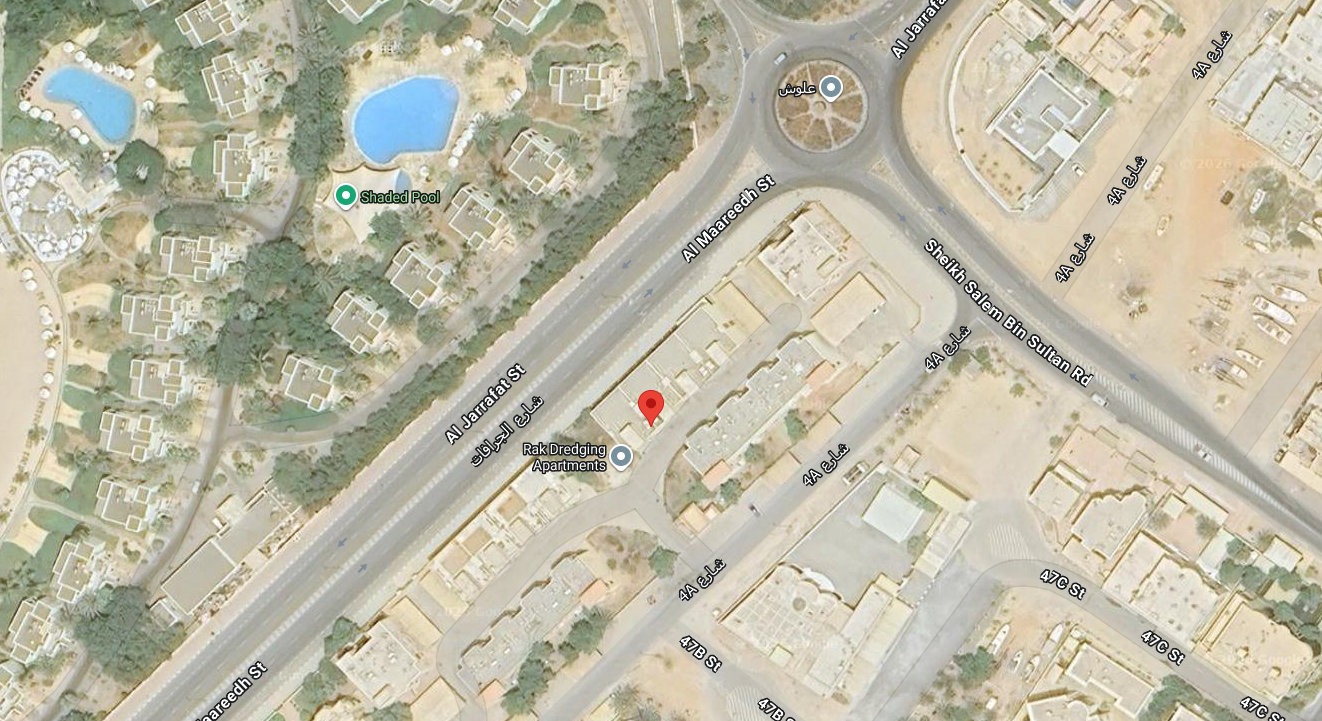
Thank you to @KeyserSoze1337 for the location info
Adem El Adeb still lives in UAE today.
Pryx has been infected by many info stealers such as RedLine and MetaStealer which is great for our analysis. Observed Usernames: adam, ademn. Adem also goes by Adam.
Sophisticated threat actors practice good opsec and never use their own PII for cybercrimes.
ademnoob214@gmail.com
adameladeb2007@gmail.com
adamlll@gmail.com
ademeladeb15l@hotmail.com
adam.adab@gmail.com
adameladeb@gmail.com
idevsenior@gmail.com
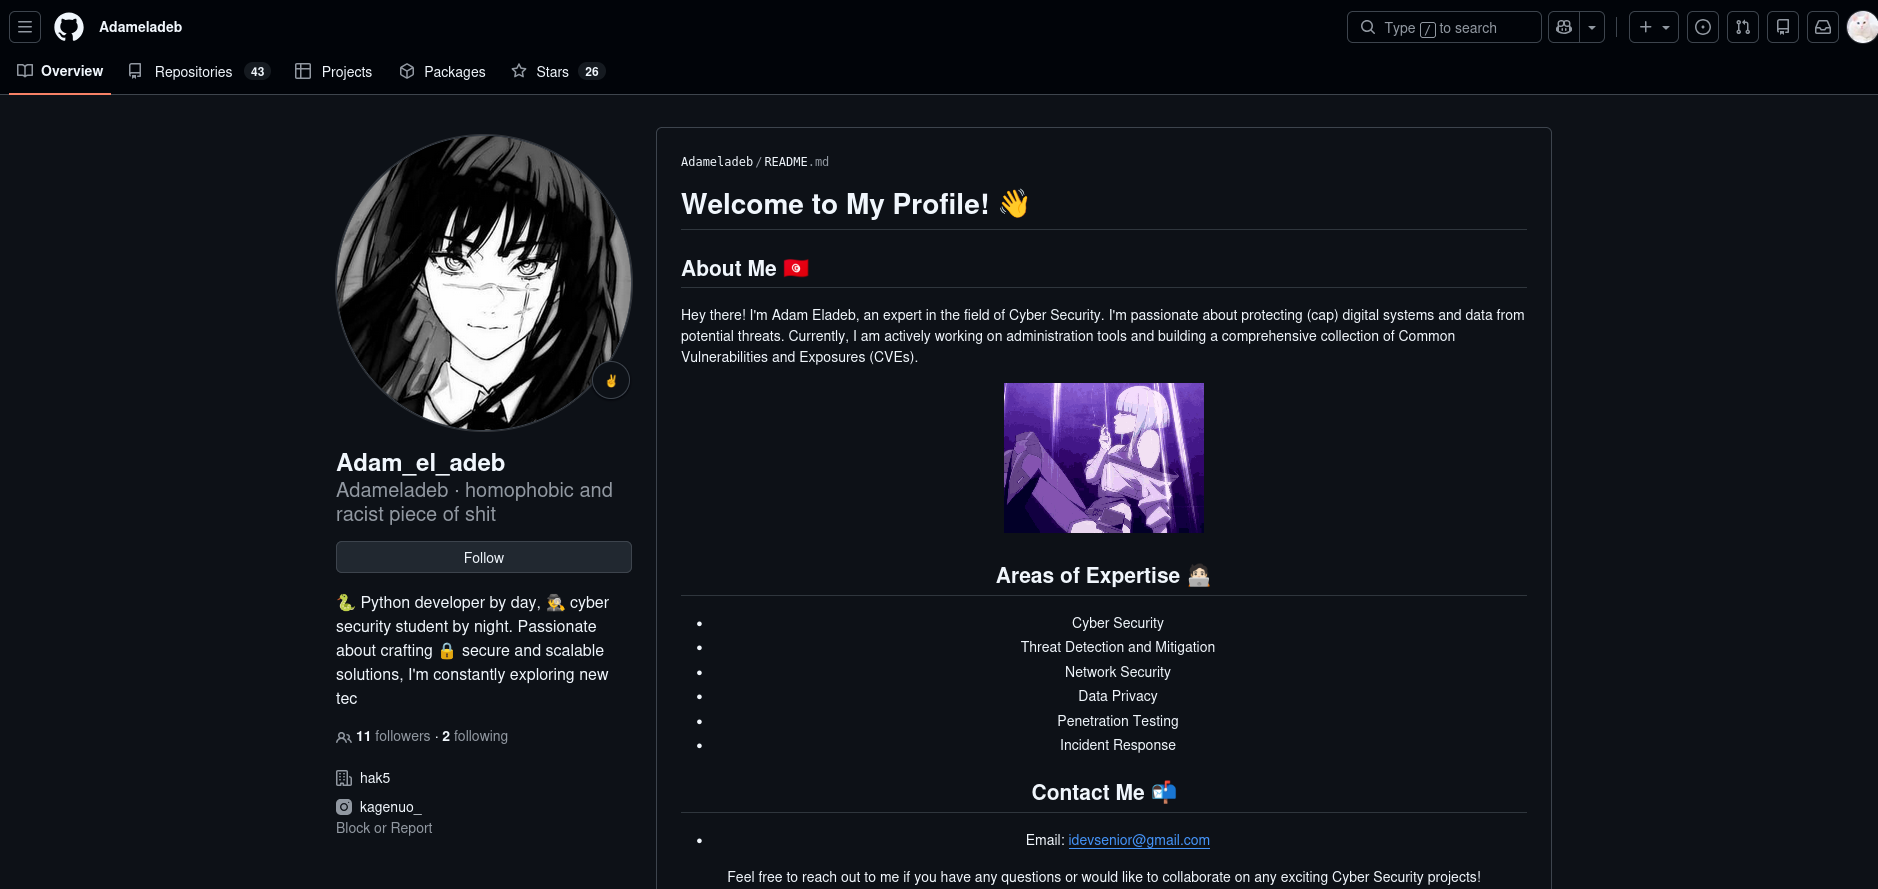
https://replit.com/@Adameladeb
"Welcome to My Profile! I am homophobic and racist piece of shit. Currently, I am actively working on ... CVEs"
|
|
|
LinkedIn https://ae.linkedin.com/in/adam-el-adeb-679b973a5
This is present day Pryx. Look at him all grown up now with great taste in fashion earrings. Present day pryx attended Black Hat MEA 2025 in Riyadh to possibly talk with others about his CVE work.
Adem El Adeb - Published CVE
Adem finally achieved his first CVE.
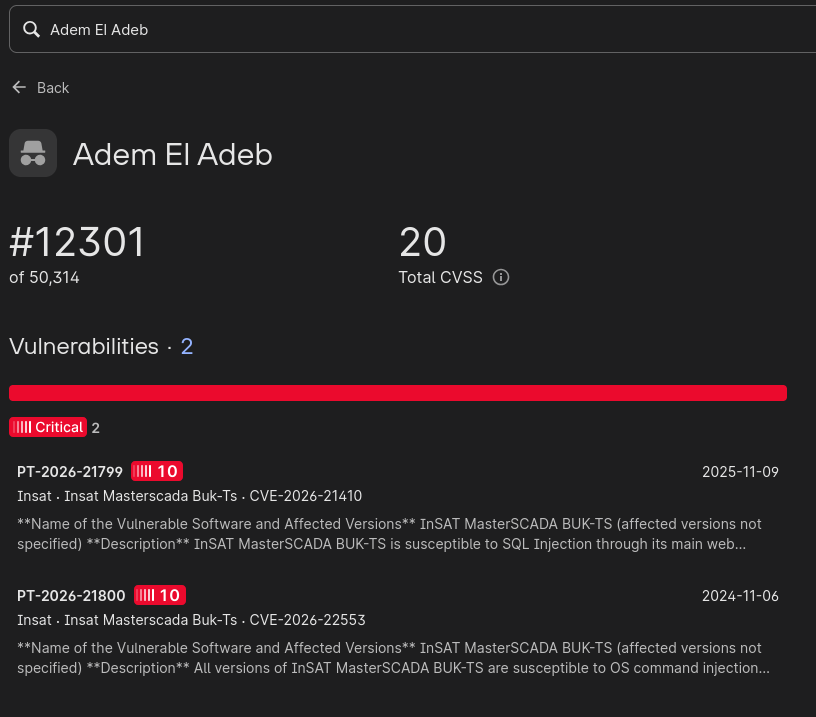
Adem El Adeb is a security researcher who reported multiple critical vulnerabilities in InSAT MasterSCADA BUK-TS to the Cybersecurity and Infrastructure Security Agency (CISA) in February 2026.
Key Findings Reported:
CVE-2026-21410: An SQL injection vulnerability in the main web interface that could allow remote code execution.
CVE-2026-22553: An OS command injection vulnerability in the MMadmServ web interface, allowing for potential remote code execution.
These vulnerabilities affect all versions of the InSAT MasterSCADA BUK-TS software, which is used in critical infrastructure sectors, including energy and water management. CISA issued an advisory (ICSA-26-055-01) based on these reports on February 24, 2026.
https://www.cisa.gov/news-events/ics-advisories/icsa-26-055-01
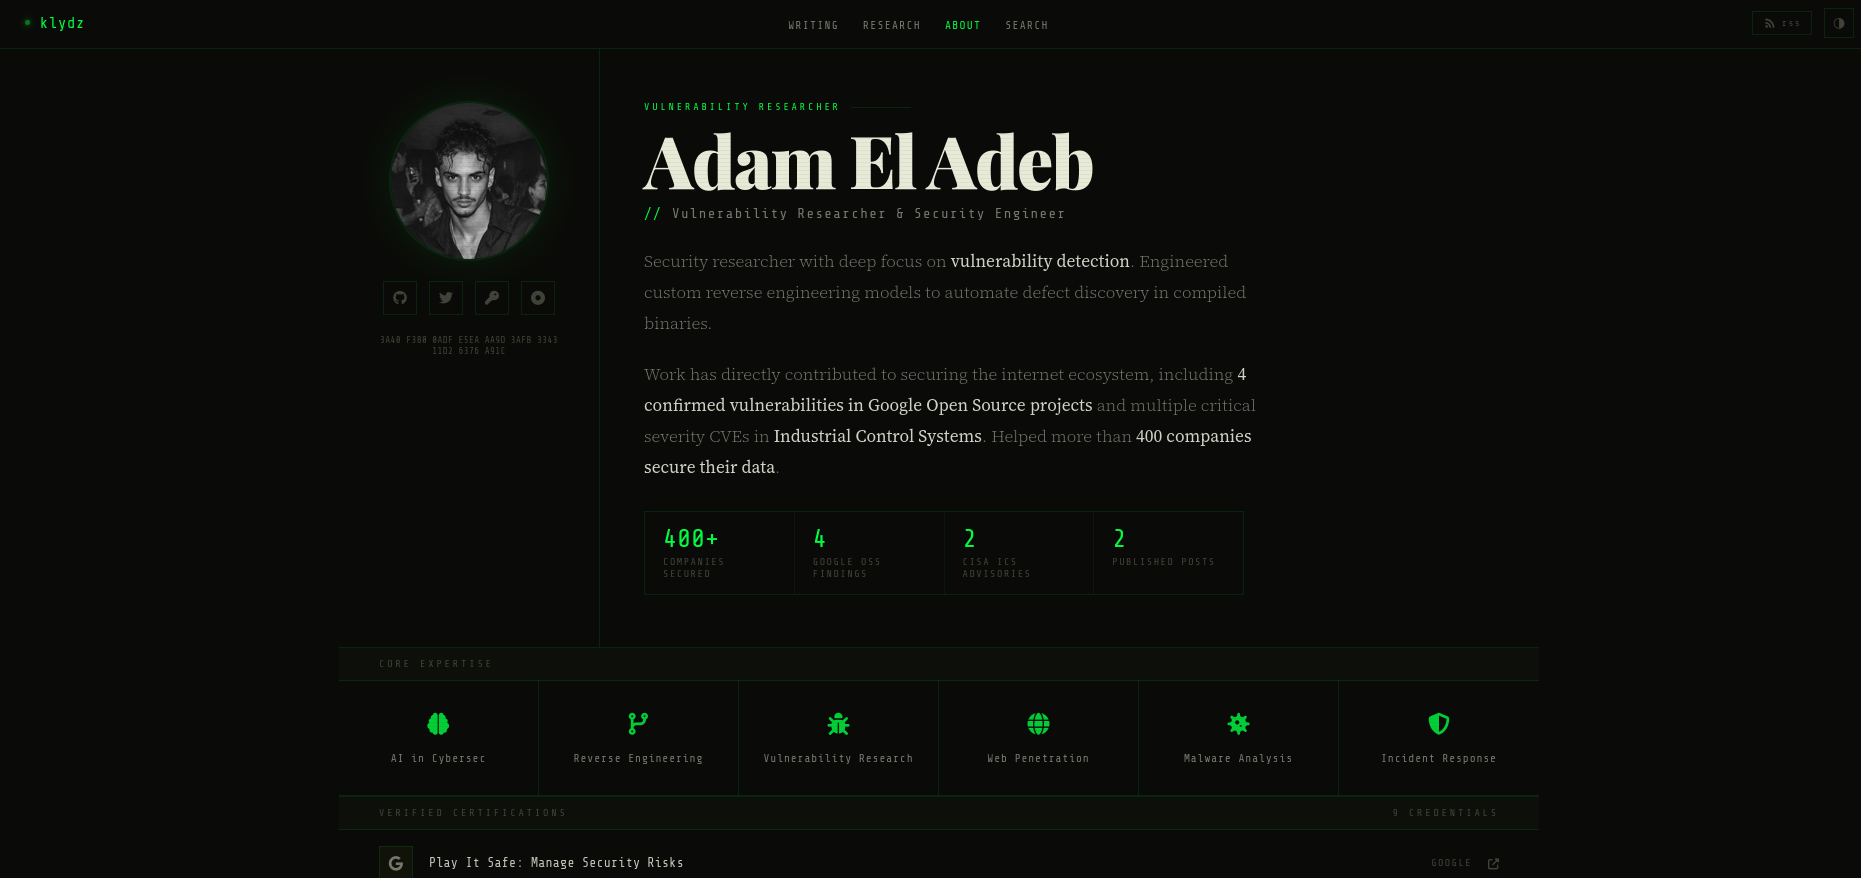
Adam El Adeb website is klydz.net
Adem El Adeb Killed 4 People?
Pryx like Industrial Control Systems as you can see by his 2 Shiny CVE trophies. He enjoys OT networks that he does not own like the SCADA network of Telecom Egypt where an alleged hacker-caused fire broke out 7 July 2025, killing 4 and injuring 27
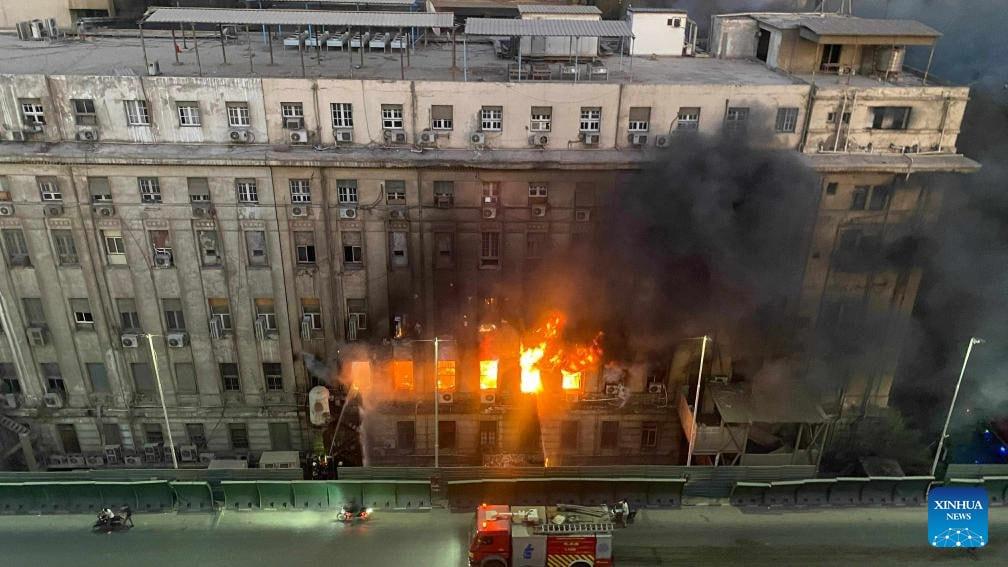
"I wouldn't post it if it wasn't true" pryx said. "I was in the network my nigga"
|
|
|
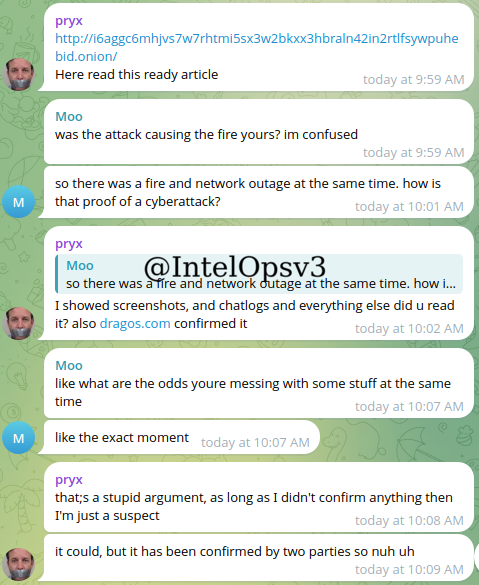
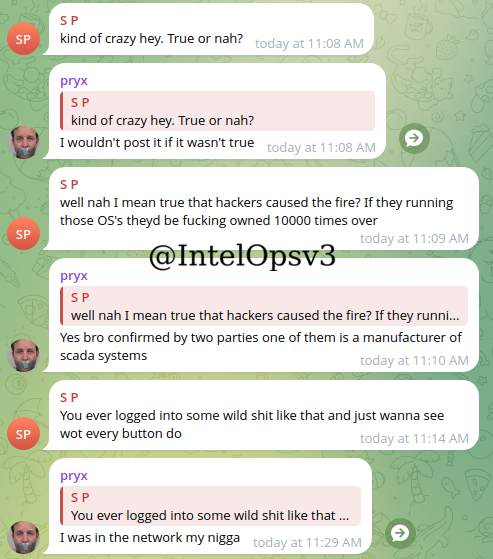
Pryx writes about the Ramses Central Exchange Fire and never published the promised follow up articles after we shined a light on him on our X account
Skiddies Larping Shiny Hunters
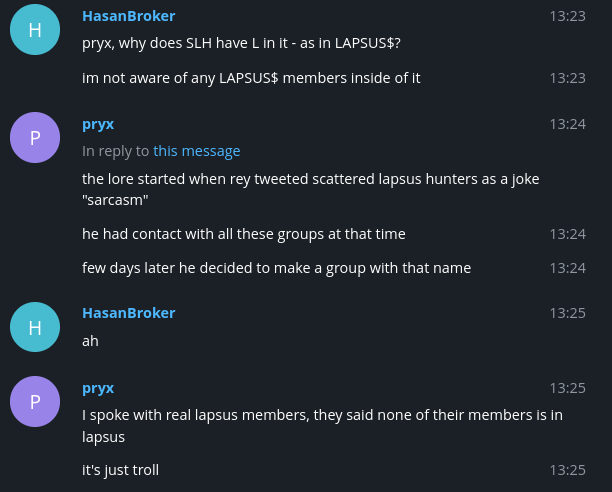
There is no Lapsus with SLSH. There is no Shiny Hunters with SLSH. SLSH is simply larping these names for clout. IntelOps suspects that SLSH is simply a rebrand of Hellcat with added members.
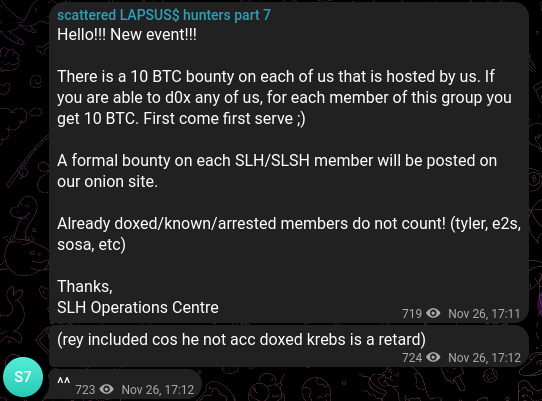
SLSH created a 10 BTC on each of them that is hosted by them. Rey increased the bounty to 15 BTC.
By our calculations SLSH now owes us 30 BTC Bounty. 15 BTC for Rey and 15 BTC for Pryx. We are coming for the remainder of you and we will not stop until you pay your bounties. Best to pay now before we add another 15 BTC bounty soon in our collection.
Pryx, our best friend, you may pay the 15 BTC bounty to our monero address:
8AVbmNAmWjS9jEHKKr29oxTxrBPgQL2o661egbDb26hxF5NbCwUdq2dFAzKZcYTiZ7jckQE6iiRdTPpmUCT4ohWGAYDxuPS
We graciously accept monero tips and donations to fund our ongoing research and infrastructure and caffeine.
Support our ongoing work with a Monero tip: