
How to Select the Best IT Security Services for Your Company
Why Every Business Needs Endpoint Protection Services (And What to Evaluate First)
By Endpoint · 2026-07-30
How many endpoints are connected to your business network right now? Counting laptops and servers is a standard starting point, but the perimeter today includes smartphones, tablets, IoT sensors, and even cloud workloads that assume device identities. Each of these access points represents a potential entry vector for an attacker. Traditional antivirus software, which relies heavily on signature updates, is consistently outpaced by fileless malware and zero-day exploits that leave no traditional footprint. Modern endpoint protection services provide a layered defense that combines prevention, detection, and automated response, fundamentally shifting the security model from reactive to proactive. The core question every IT manager and business owner must ask is whether an unmanaged endpoint could cripple their entire operation before their current defenses even register a threat.
The reality is that a single compromised credential on a corporate laptop can lead to lateral movement across the entire network, resulting in data exfiltration or ransomware deployment. This is not merely a technical inconvenience but a direct business continuity risk. The need for robust endpoint security services has moved from the realm of optional IT spend to a foundational component of enterprise risk management. With regulatory frameworks like GDPR, HIPAA, and PCI-DSS placing direct liability on data custodians, the failure to implement adequate endpoint protection can result in significant fines and reputational damage. When this becomes a priority, customized cybersecurity services for business can make a real difference to your results.
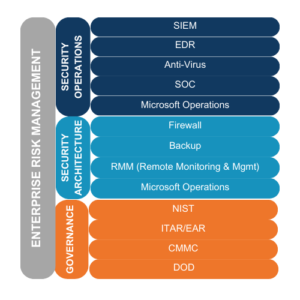
The question is no longer if a business needs endpoint protection, but how to select and implement a service that aligns with their specific operational reality, workforce structure, and risk tolerance. <> Understanding the core capabilities and deployment models available is the first step toward building a resilient security posture that does not hinder productivity but actively enables safe business growth.
Key Takeaways
- Endpoint protection has evolved beyond antivirus into integrated EPP and EDR platforms that detect behavioral anomalies.
- Choosing between cloud-native and on-premises services depends on specific data residency, latency, and compliance requirements.
- A phased implementation roadmap that includes staging, tuning, and training is essential for a successful deployment.
- Managed Detection and Response (MDR) options allow organizations without a 24/7 SOC to access advanced threat hunting capabilities.
- Evaluating provider integration with existing SIEM, SOAR, and IT service management tools is critical for operational efficiency.
How Has the Threat Landscape Made Standard Antivirus Obsolete?
The cyber kill chain has evolved significantly beyond the era of macro viruses and email attachments with executable payloads. Attackers now employ sophisticated living-off-the-land (LOTL) techniques, using trusted system binaries like PowerShell, WMI, and MsBuild to carry out malicious actions. Because these binaries are signed by Microsoft and often whitelisted, standard antivirus solutions that scan for known malicious file hashes or suspicious file structures are effectively blind to them. This is similar to a security guard who checks bags at the door but ignores an intruder who is already inside wearing a stolen uniform.
Modern endpoint detection and response (EDR) platforms, which form the core of today's endpoint protection services for enterprises, monitor behavioral patterns instead of relying solely on signature matching. A typical attack chain might begin with a phishing email containing a link to a legitimate cloud storage service where a malicious script is hosted. When the user clicks the link and runs the payload, the script might execute a series of commands that look like routine administrative activity. Traditional antivirus views each action in isolation and sees nothing wrong. An EDR engine, however, correlates the entire process tree, connecting the web browser download to the script execution to the outbound network connection to an unknown external IP address. The practical difference is profound: where legacy AV waits for the bomb to detonate, modern endpoint protection watches the behavior leading up to the explosion and intervenes in real time. It pays to weigh up endpoint security services before you commit to a setup.
Consider a hypothetical scenario where an attacker uses a PowerShell command to download a second-stage payload that mimics legitimate administrative activity. An EDR service immediately flags the anomalous process lineage, isolates the host from the network, and terminates the process—all within seconds. This automated containment is the difference between a minor alert and a full-blown data breach. <> The shift from reactive signature scanning to continuous behavioral analysis represents a fundamental change in how businesses must think about endpoint security services. Organizations still relying on legacy antivirus are essentially leaving their front door unlocked, assuming that the visible threats are the only ones that exist.
What Are the Core Capabilities of a Modern Endpoint Protection Service?
Understanding the core components of a robust endpoint protection platform (EPP) is essential for making an informed purchasing decision. These platforms have evolved into integrated stacks that combine several distinct capabilities into a single, lightweight agent. The first layer is prevention, which includes next-generation antivirus (NGAV) that uses machine learning to identify never-before-seen malware, exploit prevention that shields vulnerable applications, web filtering that blocks access to malicious URLs, and device control to manage USB and peripheral risks. Without this foundation, the network is exposed to the most basic, yet still effective, attack vectors.
The second critical layer is detection. This is where the service distinguishes itself from standard antivirus. Continuous monitoring of endpoint activity generates a constant stream of telemetry that is analyzed against global threat intelligence feeds and behavioral baselines. When an anomaly is detected, such as an unexpected registry modification or a process attempting to access the system's credential store, the platform generates an alert. In more advanced implementations, this detection triggers automated response actions, such as killing the offending process, isolating the endpoint, or rolling back file changes to a state before the infection occurred. The ability to perform a forensic rollback is particularly valuable, as it allows IT teams to reverse the effects of ransomware without needing to restore from potentially outdated backups. Options such as endpoint security services help keep everything running smoothly here.
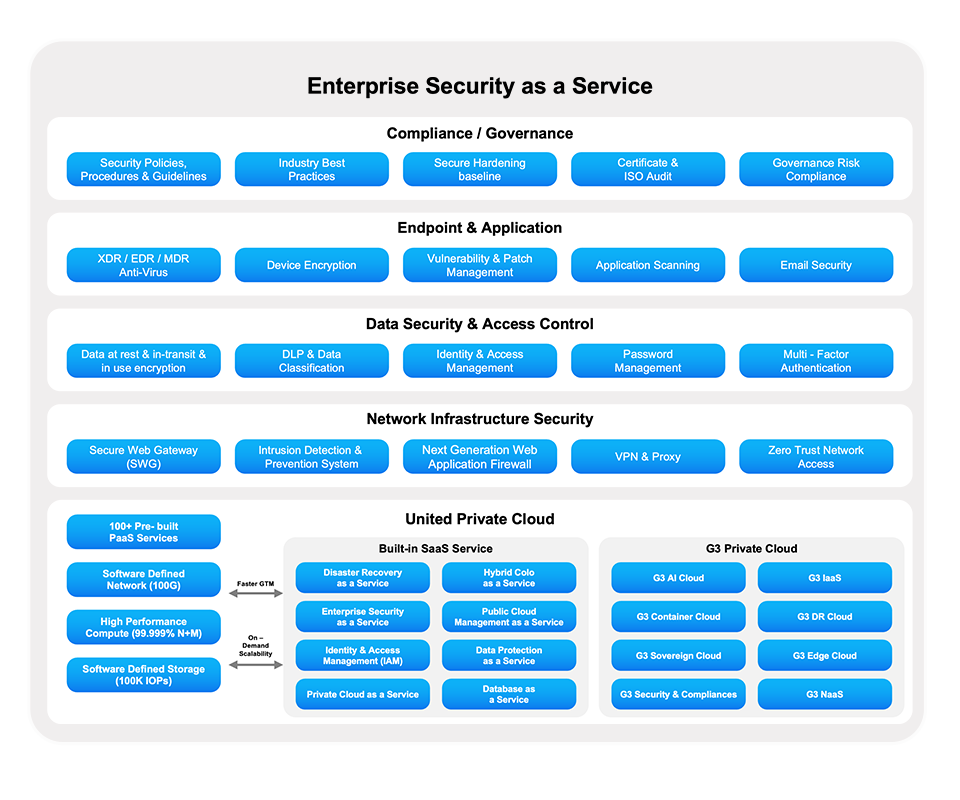
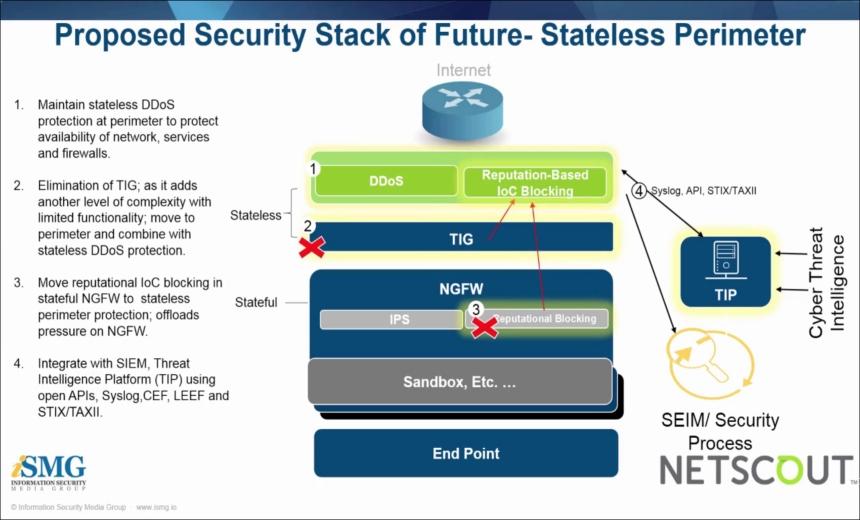
The final layer is management and integration. Managing multiple vendors for prevention, detection, and response is inefficient and creates blind spots. Consolidating on a single business endpoint security solutions simplifies the stack and reduces the mean time to identify a breach. <> A unified console provides a single pane of glass for managing all endpoints, regardless of whether they are on the corporate network or halfway around the world. Integration with existing security information and event management (SIEM) systems and IT service management (ITSM) platforms ensures that alerts are contextualized and that incident response workflows are automated. For IT managers, this consolidation translates directly into less alert fatigue, faster investigation times, and a clearer view of the organization's overall security health.
On-Premises vs. Cloud-Endpoint Security: Which Architecture Fits Your Business?
The architectural choice between cloud-native and on-premises deployment is one of the most consequential decisions an IT manager or business owner will make. Each model offers distinct advantages and trade-offs that directly impact operational overhead, data control, and scalability. The decision should be driven by concrete business requirements rather than general industry trends. A financial institution handling sensitive trading data may prioritize absolute data sovereignty, while a fast-growing SaaS startup may prioritize rapid deployment and minimal internal maintenance.
When does a cloud-native solution make the most sense?
Cloud-native endpoint protection services are delivered through a software-as-a-service (SaaS) model, where the management console, threat analytics engine, and storage for telemetry data are hosted by the vendor. These solutions offer rapid scalability, allowing organizations to protect a handful of endpoints today and thousands tomorrow without provisioning additional servers. Lower upfront capital expenditure and automatic, vendor-managed updates ensure that the organization is always protected against the latest threats without internal IT overhead. For businesses with a distributed workforce, where employees connect from various locations and networks, a cloud-native solution provides consistent policy enforcement and visibility regardless of physical location. The trade-off is that the organization depends on the vendor's security controls for its telemetry data and must trust the vendor's infrastructure uptime.
What are the arguments for keeping security infrastructure on-premises?
On-premises deployment keeps all management infrastructure, endpoint telemetry, and data storage within the organization's direct control. This is essential for organizations operating under strict data residency regulations, air-gapped environments, or companies with ultra-low latency requirements for detection and response actions. The primary advantage is absolute control over who has access to the sensitive metadata and process histories generated by the security tools. However, this control comes at a cost. The organization must bear the full burden of server maintenance, software patching, capacity planning, and high availability configuration. Scaling the solution requires procuring, racking, and configuring additional hardware.
Choosing between cloud and on-premises endpoint protection is not just a technological decision; it is a strategic business alignment that reflects an organization's tolerance for shared risk versus its need for absolute control over its security telemetry.
| Aspect | Cloud-Native (SaaS) | On-Premises | Hybrid / MDR |
|---|---|---|---|
| Deployment Speed | Rapid (minutes to hours) | Slow (weeks to months) | Rapid (days) |
| Scalability | Highly elastic, on-demand | Limited by hardware procurement | Flexible via provider |
| Data Control | Vendor managed infrastructure | Full customer control | Shared responsibility |
| Maintenance | Low (Vendor handles all patching) | High (Internal IT required) | Low (Provider handles infrastructure) |
| Ideal for | Distributed teams, startups, rapid growth | Regulated, air-gapped environments | Organizations needing managed expertise |