
Who Runs Qilin? Identifying Haise
Qilin was the most active ransomware group of 2025–2026 by number of victims. Behind the brand is a structured ransomware-as-a-service operation comprising administrators, affiliates, developers, and its own infrastructure. Researchers have long identified a user operating under the alias Haise as the group's public face. However, establishing someone's public role and establishing their real identity are two different tasks. What follows is a chain of data linking the alias Haise to a specific individual.
The foundation of this investigation is a consistent and robust chain of accounts and identifiers that can be traced independently in both directions: from Qilin's public administrator to a real name, and from that name back to digital activity within the ransomware ecosystem.

Haise: Qilin's Public Administrator
Haise appeared on the criminal forum RAMP on May 29, 2022. By February 2023, he was openly advertising Qilin's affiliate program. In July, he described the financial arrangement in detail: ransom payments were sent to affiliates' wallets, after which affiliates transferred a share, typically 15–20%, to the operators.
In July 2024, he continued recruiting members on RAMP. In the spring of 2025, he returned to the public spotlight. On April 1, he announced a new ransomware release and a DDoS feature in the affiliate panel. In June, he promoted the "Call lawyer" option, a tool designed to pressure victims during ransom negotiations.
Reports by Group-IB, SANS, Halcyon, and other organizations consistently describe Haise as an administrator and key Qilin operator.
From the Haise Alias to Profiles on Other Forums
RAMP is a closed criminal platform without open registration. Each new participant had to provide profiles from other hacking forums or pay a cryptocurrency fee of $400. An account was activated only after verification.
In private conversations, the forum administrator (admin) and his assistant (Nowheretogo) coordinated the approval of new users. The assistant submitted lists of usernames and profiles, and the administrator approved them.
Haise appears twice in the approval records, both times with profiles on other platforms.
In the first list, dated June 3, 2022, the username haise is matched, in the corresponding order, with the following Exploit profile:
/profile/113584-alexbigboss44/
In the second list, dated June 21, 2022, Haise is matched with an XSS profile:
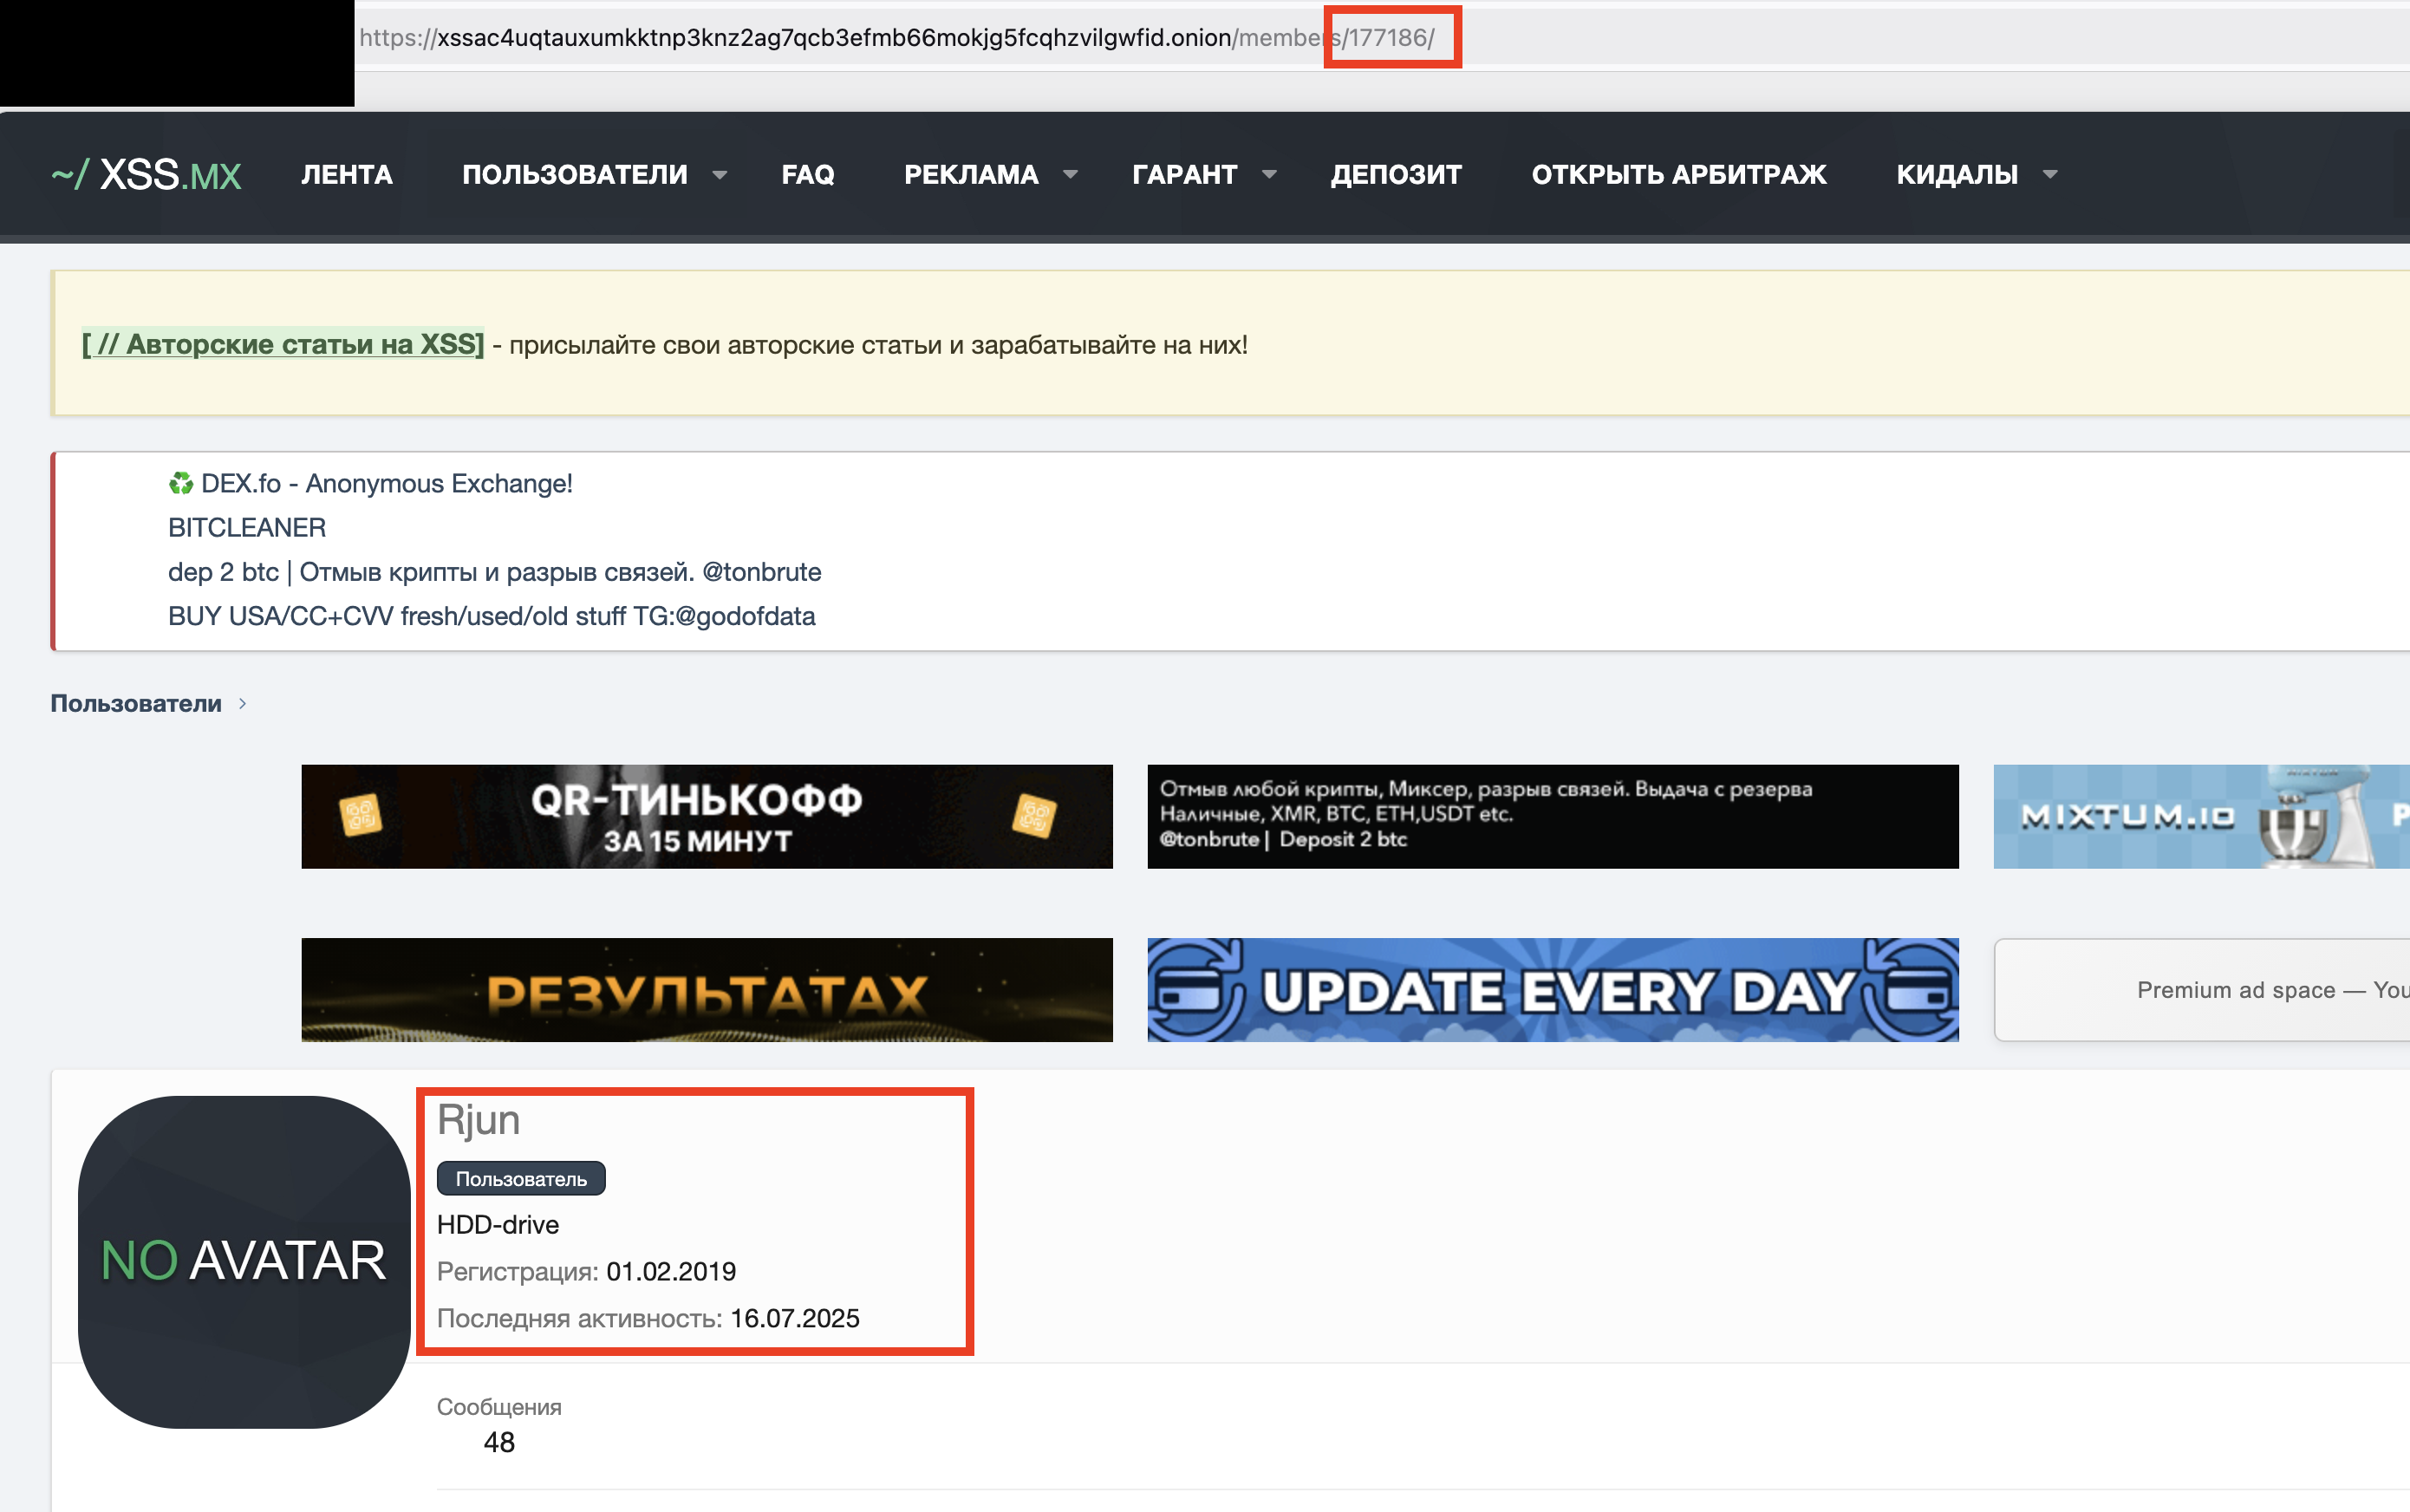
/members/177186/
The first record
The message below lists ten RAMP applicants, followed in the corresponding order by ten existing Exploit.in profiles.
[SCREENSHOT: RAMP approval record dated June 3, 2022]
The original record:
[2022-06-03 17:42:51 UTC] Nowheretogo (12) | message_id=1990
============================================================
Please approve--->>> SpLo1t, topbood, Amandirey, Undermine, odinsmokes, W999a!, polosatiy77,
sourskittles, haise, Swift.
============================================================
Profile Exp:

/profile/55267-redsnow/
/profile/130542-goodshmoneyy/
/profile/110612-amandirey/
/profile/120883-undermine/
/profile/125444-0dinsmokes/
/profile/124656-69pdf/
/profile/106300-polosatiy/
/profile/103729-tngrak/
/profile/113584-alexbigboss44/
/profile/130415-swift_/

[2022-06-03 17:48:12 UTC] Nowheretogo (12) | message_id=1993
I invited Bank Injector and Sql injector Coder name "[B]Stillam[/B]" from Exploit forum
his Ramp nick also same --->>[B]Stillam

waiting approval[/B]

[2022-06-04 20:19:50 UTC] admin (1) | message_id=1996
Have approved everyone, and [B]Stillam too, EXCEPT Swift. No user Swift found[/B]
The second record
The message lists nineteen RAMP applicants, followed in the corresponding order by nineteen existing XSS.is profiles.
[SCREENSHOT: RAMP approval record dated June 21, 2022]
[2022-06-21 11:57:27 UTC] Nowheretogo (12) | message_id=2104
===============================================================
Please Approve --->>> Choppi77, odinsmokes, topbood, soibten.2210, "Haise, ggho5t, Anunnack, lighter133,
===============================================================
r3dru9, cortexxx.2257, Morovic, b4ssb4b33, doodoonow.2186, ZEON, MNSTR, killerAV, coomboy, braked.2312, Perecrestock
================================================================

[B]Xss Profile:[/B]

/members/215839/
/members/255039/
/members/264274/
/members/238719/
/members/177186/
/members/264570/
/members/239042/
/members/256639/
/members/258722/
/members/233888/
/members/212682/
/members/217424/
/members/264240/
/members/209317/
/members/181544/
/members/190951/
/members/257475/
/members/260430/
/members/239820/

[2022-06-21 14:44:08 UTC] admin (1) | message_id=2106
Have activated: Choppi77, soibten.2210 (no soibten.2210, I actvated soibten), ggho5t, Anunnack, lighter133, r3dru9, cortexxx.2257 (no cortexxx.2257, I activated cortexxx), Morovic, b4ssb4b33, doodoonow.2186 (no doodoonow.2186, I activated doodoonow), ZEON, MNSTR, killerAV, coomboy, braked.2312 (no braked.2312, I activated braked), no user Perecrestock, I acticated pereckrestock
were already activated, i did nothing on those: odinsmokes, topbood, Haise
This establishes two other profiles associated with Haise:
-
Exploit profile: /profile/113584-alexbigboss44/
-
XSS profile: /members/177186/
The XSS profile uses the username Rjun.
On Exploit, the user behind /profile/113584-alexbigboss44/ listed the Telegram contact @alexbigboss44 in another account, /profile/84170-rjun/.
Thus, the alias Rjun is independently confirmed as another username used by Haise across two different platforms.
From the Rjun Alias to an Email Address
The Rjun profile on the BHF forum contains the email address mail-30a@mail.ru.
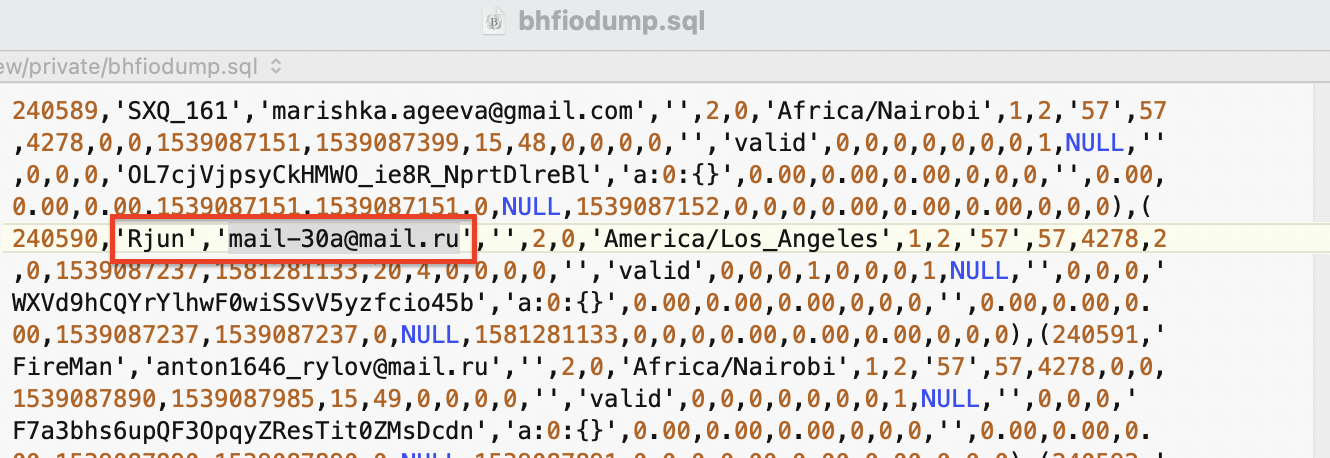
[SCREENSHOT: BHF database record]
The same email address was used during registrations on the Zloy hacking forum by a user named rjun123.
The following record comes from the Zloy.org data leak.
The database entry contains:
Date: 2015-12-09
Email: mail-30a@mail.ru
IP: 95.140.92.59
LastActive (UNIX): 1449697736
NickName: Rjun123
RegDate (UNIX): 1449697721
[SCREENSHOT: Zloy.org database record]
(The Zloy.org forum dump contains data from approximately 25,000 accounts. The archive is dated 2016. The database included IP addresses, email addresses, usernames, dates, activity information, and salted MD5 password hashes).
From the Email Address to a Real Person
The same email address, mail-30a@mail.ru, appears in a leaked database associated with Russia's public services portal, which began circulating in early 2025. The database reportedly contains approximately 180 million records, including full names, telephone numbers, email addresses, tax identification numbers, SNILS numbers, passport details, and residential addresses.
The record identifies:
Address: [REDACTED]
Email: mail-30a@mail.ru
Full name: Alexey Mikhailovich Yakovtsev
Passport: [REDACTED]
Phone: [REDACTED]
SNILS: [REDACTED]
В утечке Gosuslugi 2024 присутствует Запись:
• Address: г Санкт-Петербург, п Парголово, ул Заречная,45 ******[REDACTED]
• Email: mail-30a@mail.ru
• FullName: яковцев алексей михайлович
• Passport: 4710 278***[REDACTED]
• Phone: 79523796278
• Snils: 15472635778 [REDACTED]
[SCREENSHOT: Relevant database record, with sensitive personal identifiers redacted]
(In early 2025, a database reportedly obtained from the Russian public services website began circulating online. The leak was said to contain 180 million records and to cover practically the entire Russian population. It included full names, telephone numbers, email addresses, tax identification numbers, SNILS numbers, passport numbers, and residential addresses.)
Thus, the email address mail-30a@mail.ru directly leads to Alexey Mikhailovich Yakovtsev, born on August 18, 1990.
[PHOTO: Images from 2010 and 2015. Obtained from the Himera Search Pro information system.]
The overall investigative chain
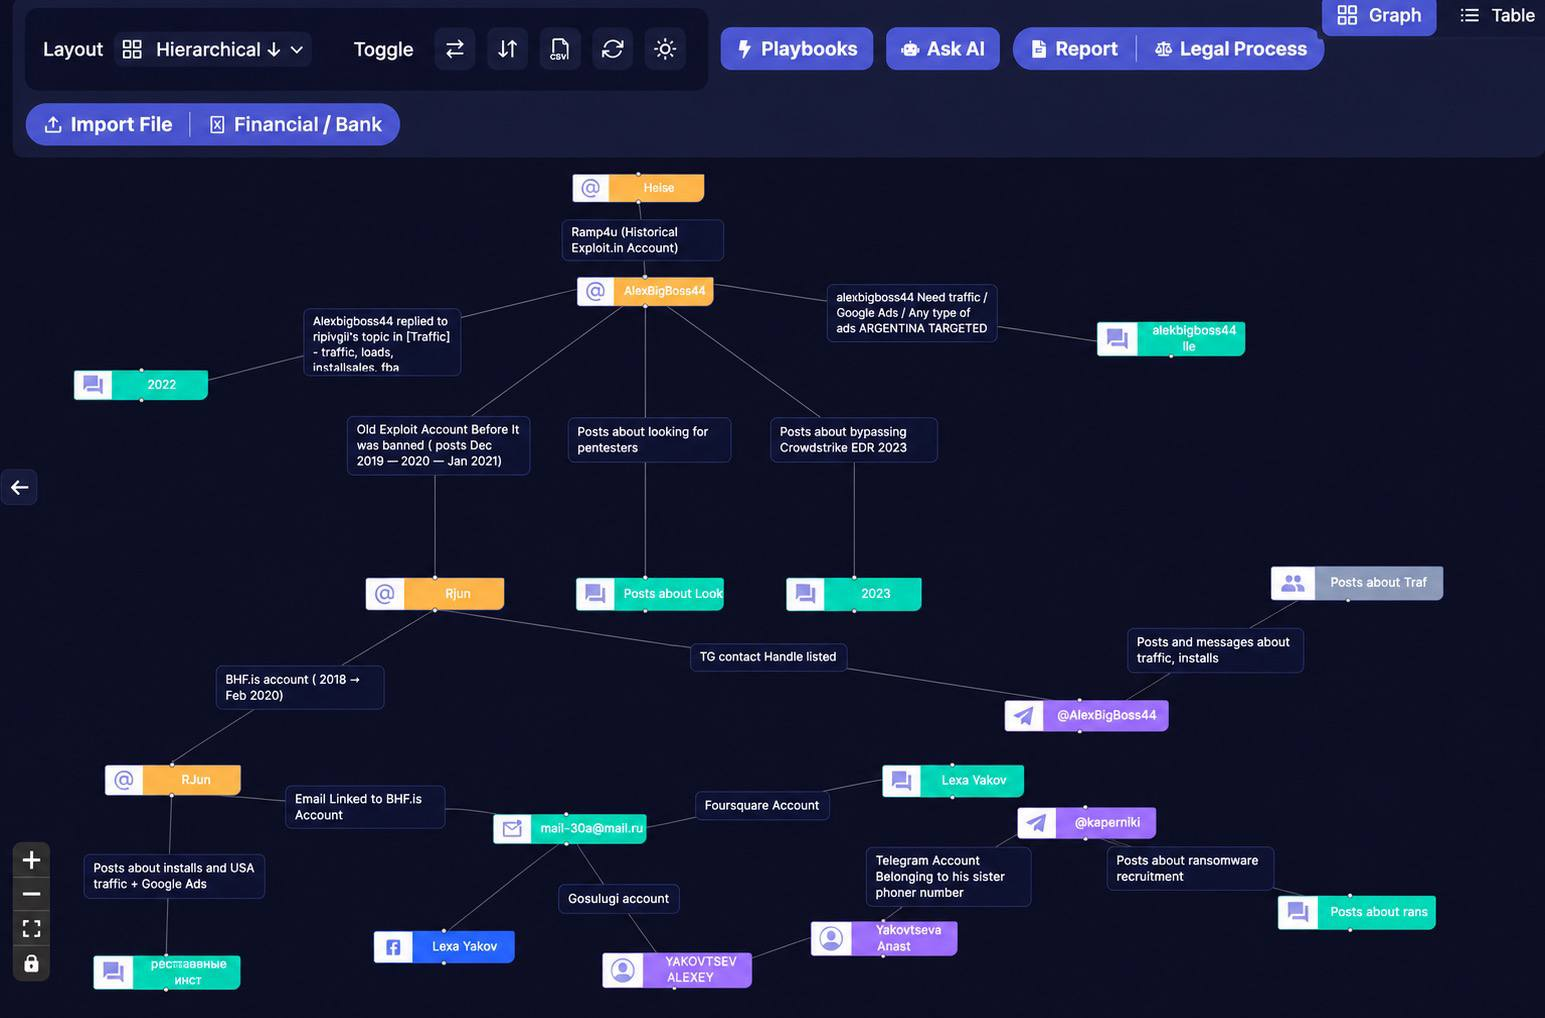
[IMAGE: Investigation linkage diagram. The search for identifiers and connections was conducted using the IntelHawk.ai platform.]
Reverse Chain: From Yakovtsev's Identity to the Ransomware Ecosystem
A reverse examination, starting with the individual's identity and tracing back to the group, further supports the connection.
A search of leaked databases using the Sherlock bot @Sherlock_GangIntel_bot for the query "YAKOVTSEV ALEXEY MIKHAILOVICH 18.08.1990" identifies his biological sister: Anastasia Mikhailovna Yakovtseva, born October 13, 1992.
A telephone number +79602347275 registered to her is associated with the email addresses aleksey1990yakov@mail.ru and rjun123321@mail.ru (the Rjun alias appears again), as well as the Telegram account @kaperniiki, ID 118329521.
Telegram account activity
Account status: deleted.
Public messages in Telegram groups document activity between September 15, 2018, and July 29, 2024.
The message history from source @imsg_bot ID 118329521 reveals a consistent profile of interests:
-
Ransomware. Participation in the Ransomware Developers group, discussions about bypassing EDR solutions such as CrowdStrike, searching for source code, and evaluating the cost of locker development.
-
Advanced technical topics. Messages such as "Guys, who knows how the ESXi kernel works?" and "Does anyone write libraries in pure C?"
-
Major underground platforms. Discussions about the RAMP forum and searches for similar Chinese platforms.
Characteristic messages include:
"CrowdStrike, has anyone bypassed it without a token?"
"Has anyone seen Linux source code for ESXi ransomware on GitHub?"
"Who works with corporate targets?"
"We are looking for pentesters for WIN/LIN/ARM/NAS/ESXi."
ΙD: 118329521
| Дата | id сообщения | Текст сообщения | Название группы |
| 13:56:55 29.07.2024 | https://telegram.me/CobaltStrikeGroup/4229 | I understand they | Cobalt Strikers | Group |
| 13:56:06 29.07.2024 | https://telegram.me/CobaltStrikeGroup/4228 | Qilin, RansomHub ransomware added to Scattered Spider arsenal https://malware.news/t/qilin-ransomhub-ransomware-added-to-scattered-spider-arsenal/84195 |
Cobalt Strikers | Group |
| 19:15:07 01.08.2023 | https://telegram.me/ProCxx/580559 | ребят кто хорошо знает как работает ядро esxi или как обойти проблему сменив архитектуру приложения | pro.cxx |
| 22:24:42 12.07.2023 | https://telegram.me/ProCxx/576190 | Вечер добрый ребят кто нибудь пишет либы на чистом С ? | pro.cxx |
| 10:06:04 08.04.2023 | 189296 | Ищем пентестеров WIN/LIN/ARM/NAS/ESXi Отличные условия, совершенно новый софт Нужны опытные пентестеры Первый контакт в ПМ |
Рынок "1-ый Нелегальный" |
| 06:39:26 29.07.2024 | https://telegram.me/ransomwaredevs/52744 | eldorado can't even be called a locker ) | Ransomware Developers |
| 14:02:39 28.07.2024 | https://telegram.me/ransomwaredevs/52669 | скинь в личку | Ransomware Developers |
| 14:02:01 28.07.2024 | https://telegram.me/ransomwaredevs/52667 | китайский площадок нету на подобе рампы? | Ransomware Developers |
| 10:40:56 24.10.2023 | https://telegram.me/ransomwaredevs/31132 | вроде срач был на хсс по этому поводу | Ransomware Developers |
| 10:40:34 24.10.2023 | https://telegram.me/ransomwaredevs/31131 | а не кодер случаем первый слил билд? | Ransomware Developers |
| 18:33:15 26.08.2023 | https://telegram.me/ransomwaredevs/27635 | кто по корпам работает? | Ransomware Developers |
| 14:38:44 10.08.2023 | https://telegram.me/ransomwaredevs/27239 | Ну если бы его только в ручную отрубали тогда сетки мертвым грузом с ним лежали , а их покупают | Ransomware Developers |
| 14:36:54 10.08.2023 | https://telegram.me/ransomwaredevs/27232 | да и через инсталлы, сплойты , брут Единственное пока с почтовиками не разобрался | Ransomware Developers |
| 14:34:25 10.08.2023 | https://telegram.me/ransomwaredevs/27228 | пока ищу кто с этим ав работает | Ransomware Developers |
| 14:31:52 10.08.2023 | https://telegram.me/ransomwaredevs/27221 | как то же отрубают или обходят не понятно как Причем корпы именно с этим ав покупают | Ransomware Developers |
| 14:27:01 10.08.2023 | https://telegram.me/ransomwaredevs/27216 | CrowdStrike кто не будь обходил без токена? | Ransomware Developers |
| 17:45:29 10.07.2023 | https://telegram.me/ransomwaredevs/26109 | никто исходники линокса с эскси не видел на гитхабе ранса ? | Ransomware Developers |
| 23:13:11 08.07.2023 | https://telegram.me/ransomwaredevs/26026 | ДНС домен конечно подсвечивает но держиться херого и длл не прогрузить в память только роняю на стол | Ransomware Developers |
| 23:12:04 08.07.2023 | https://telegram.me/ransomwaredevs/26024 | амадей чет не фантан | Ransomware Developers |
| 14:03:18 08.07.2023 | https://telegram.me/ransomwaredevs/25585 | вот я и говорю если файлы зашифрованы пятнами по всему файлу , скорее всего он выдерет только куски | Ransomware Developers |
| 10:34:49 21.04.2024 | 101205 | на сентинел нету ? | Ralf Hacker Public Chat |
| 14:19:37 10.08.2023 | 96279 | ребят как отключить CrowdStrike | Ralf Hacker Public Chat |
| 16:59:27 14.05.2023 | 94765 | есть у кого китайские форумы на подобе рампа? | Ralf Hacker Public Chat |
| 16:41:12 13.05.2023 | 94691 | хотел уточнить выплаты у всех просели или нет) | Ralf Hacker Public Chat |
| 16:40:15 13.05.2023 | 94689 | кто ни будь по корпам шевелиться? | Ralf Hacker Public Chat |
| 11:00:09 10.04.2023 | 42099 | а те где рансы можно?) | COOCKIE.PRO | CHAT PUBLIC |
| 10:40:46 10.04.2023 | 42093 | есть у кого список форумов где пентестеры сидят по мимо экспы , хсс , рамп? | COOCKIE.PRO | CHAT PUBLIC |
English translate
Telegram ID: 118329521
|
Date and time (UTC) |
Message ID / Link |
Message text (English translation) |
Telegram group |
|---|---|---|---|
|
13:56:55, 29 Jul 2024 |
I understand they |
Cobalt Strikers Group |
|
|
13:56:06, 29 Jul 2024 |
Qilin, RansomHub ransomware added to Scattered Spider arsenal. Source |
Cobalt Strikers Group |
|
|
06:39:26, 29 Jul 2024 |
Eldorado can't even be called a locker. |
Ransomware Developers |
|
|
14:02:39, 28 Jul 2024 |
Send it to me privately. |
Ransomware Developers |
|
|
14:02:01, 28 Jul 2024 |
Are there any Chinese platforms similar to RAMP? |
Ransomware Developers |
|
|
10:34:49, 21 Apr 2024 |
101205 |
Is there one for Sentinel? |
Ralf Hacker Public Chat |
|
10:06:04, 8 Apr 2023 |
189296 |
Looking for penetration testers specializing in WIN/LIN/ARM/NAS/ESXi. Excellent terms, completely new software. Experienced penetration testers needed. First contact via private message. |
Market "1st Illegal" |
|
19:15:07, 1 Aug 2023 |
Guys, does anyone know how the ESXi kernel works, or how to get around the problem by changing the application's architecture? |
pro.cxx |
|
|
10:40:56, 24 Oct 2023 |
I think there was an argument about this on XSS. |
Ransomware Developers |
|
|
10:40:34, 24 Oct 2023 |
Wasn't the first person to leak the build a coder, by any chance? |
Ransomware Developers |
|
|
18:33:15, 26 Aug 2023 |
Who works with corporate targets? |
Ransomware Developers |
|
|
14:38:44, 10 Aug 2023 |
If it were only being shut down manually, the networks would remain completely useless along with it. But they buy them. |
Ransomware Developers |
|
|
14:36:54, 10 Aug 2023 |
And through installers, exploits, and brute force as well. The only thing I haven't figured out yet is how to deal with email providers. |
Ransomware Developers |
|
|
14:34:25, 10 Aug 2023 |
I'm currently looking for someone who works with this antivirus. |
Ransomware Developers |
|
|
14:31:52, 10 Aug 2023 |
There must be a way to disable or bypass it, but I don't understand how. What's more, companies specifically buy systems with this antivirus. |
Ransomware Developers |
|
|
14:27:01, 10 Aug 2023 |
Has anyone bypassed CrowdStrike without a token? |
Ransomware Developers |
|
|
14:19:37, 10 Aug 2023 |
96279 |
Guys, how do you disable CrowdStrike? |
Ralf Hacker Public Chat |
|
17:45:29, 10 Jul 2023 |
Has anyone seen the Linux source code for ESXi on the Ransomware GitHub? |
Ransomware Developers |
|
|
23:13:11, 8 Jul 2023 |
The DNS domain does flag it, of course, but it doesn't hold up well. I can't load the DLL into memory; I can only drop it onto the desktop. |
Ransomware Developers |
|
|
23:12:04, 8 Jul 2023 |
Amadey isn't particularly impressive. |
Ransomware Developers |
|
|
14:03:18, 8 Jul 2023 |
That's what I'm saying. If files are encrypted in scattered sections throughout the file, it will most likely only retrieve fragments. |
Ransomware Developers |
|
|
22:24:42, 12 Jul 2023 |
Good evening, guys. Does anyone write libraries in pure C? |
pro.cxx |
|
|
16:59:27, 14 May 2023 |
94765 |
Does anyone know of Chinese forums similar to RAMP? |
Ralf Hacker Public Chat |
|
16:41:12, 13 May 2023 |
94691 |
Just wanted to check whether everyone's payouts have gone down. |
Ralf Hacker Public Chat |
|
16:40:15, 13 May 2023 |
94689 |
Is anyone working on corporate targets? |
Ralf Hacker Public Chat |
|
11:00:09, 10 Apr 2023 |
42099 |
And what about the ones where ransomware is discussed? |
COOCKIE.PRO | CHAT PUBLIC |
|
10:40:46, 10 Apr 2023 |
42093 |
Does anyone have a list of forums where penetration testers hang out, apart from Exploit, XSS, and RAMP? |
COOCKIE.PRO | CHAT PUBLIC |
[SCREENSHOTS: Telegram original messages demonstrating the account's technical interests and ransomware-related activity]
Temporal and Contextual Match: Qilin Advertising
On July 29, 2024, an account in the Cobalt Strikers group (t.me/CobaltStrikeGroup/4228) published the message:
"Qilin, RansomHub ransomware added to Scattered Spider arsenal"
One week later, a commercial advertisement for the Qilin group appeared in the same group. It offered an affiliate opportunity, described the group's advantages, and provided a Tox contact.
A search for this Tox identifier across Telegram channels returns four results.
Similar advertisements appeared in groups where Alexey was present, on the following dates:
-
July 22, 2024 (two advertisements)
-
July 29, 2024
-
August 7, 2024
Examples:
https://t.me/ransomwaredevs/52746
https://t.me/CobaltStrikeGroup/4359
Neither before nor after these advertisements does the Qilin brand appear in these groups. This can be verified through a search of the groups' message histories.
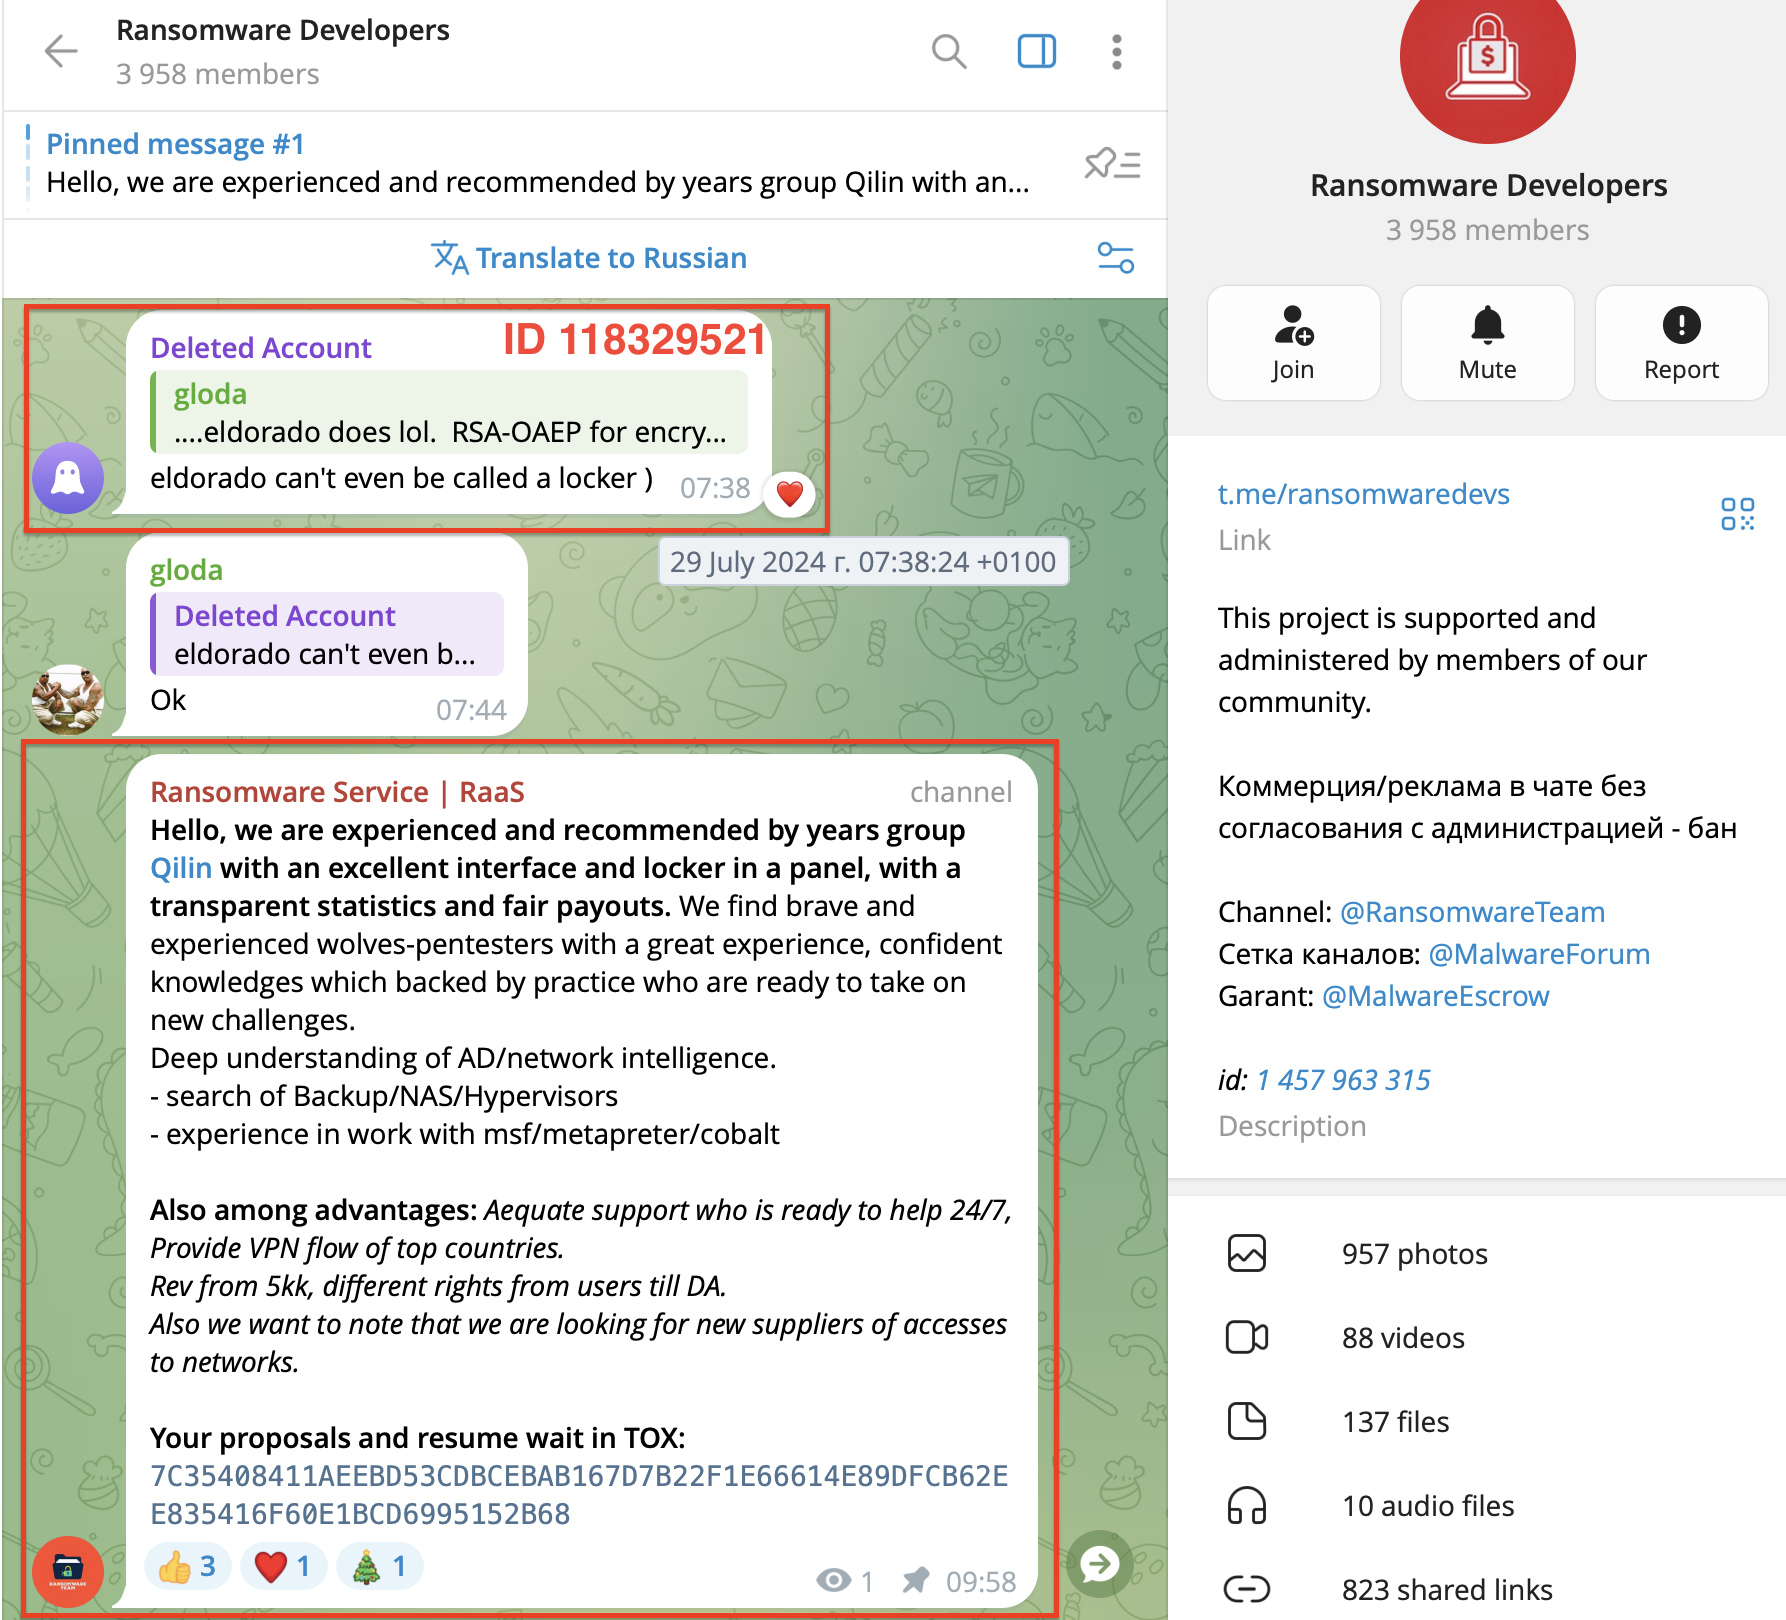
[SCREENSHOTS: Qilin advertisements and related Telegram group messages]
Confirmation of Account Ownership
A leaked Beeline subscriber database shows that the telephone number associated with the account was registered to Anastasia Yakovtseva from March 20, 2015, to October 24, 2018. The registration record contains a residential address in Murmansk, Russia. [REDACTED]
РЕГИСТРАЦИЯ
SIM-КАРТ BEELINE 2021 FB (7)
Полное имя
ЯКОВЦЕВА АНАСТАСИЯ МИХАЙЛОВНА
Телефон
9602347275
Год источника
2021
Адрес
г мурманск, ул гвардейская**********[REDACTED]
Дата активации сим-карты
20.03.2015
According to the account statistics, the Telegram account was registered no later than September 15, 2018, based on its first message in the group.
Thus, during the period in which the account was active, it was used by Alexey Yakovtsev.
Conclusion
The chain runs in one direction and is corroborated in reverse:
Haise → Rjun / alexbigboss44 profiles → mail-30a@mail.ru → Alexey Mikhailovich Yakovtsev (18.08.1990) → Telegram ID 118329521 → messages about ransomware, RAMP, and Qilin → Qilin advertisements in the same groups and on the same dates.
Each link is supported by an independent source: RAMP approval records, XSS and Exploit forum profiles, BHF and Zloy database dumps, the public services portal data leak, the Beeline subscriber leak, Telegram account statistics, and publicly available message histories.
Taken together, these data points provide a high degree of confidence that the person behind the alias Haise, Qilin's public administrator, is Alexey Mikhailovich Yakovtsev.
The full report can be downloaded here:
https://mega.nz/file/Q1w0Ea6A#ZEK3hQxrRF_VGOuOO_oaw2kCGOUq5qQsRSskYjTyVhw
File name:
Yakovtsev_Alexey_Mikhailovich_IntelHawk_Evidence_Report.pdf
118329521_messages.xlsx
881760052_messages.xlsx
alexbigboss_posts_2021-2023.txt
IntelHawk_Usage_Guide.pdf
rjun_exploit.txt
Rjun_exploit_in_forum_activity_English.txt
rjun_BHF_posts.txt
user-118329521-messages.xlsx
user-881760052-messages.xlsx
I ask that the discovery identifying Haise as Yakovtsev not be attributed to me. I personally rechecked all the materials and conclusions, cross-referenced them against independent data sources, and validated the entire chain of evidence. I stand behind this material and endorse its conclusions.
All work on the identification chain was conducted entirely on the IntelHawk.ai platform using the platform's internal sources.
__________